A US buyer sends a SOC 2 request. A German buyer sends an ISO 27001 one. Here is what each proof is, who asks for which on the auditors' own pages, what sellers publish for the cost, and when one control program can feed both.
You are a US or EU SaaS or AI startup and someone in procurement has written "please provide your SOC 2 report or ISO 27001 certificate." You need to know which one, how much, how long, and whether doing one makes the other cheap.
What is the difference between SOC 2 and ISO 27001?
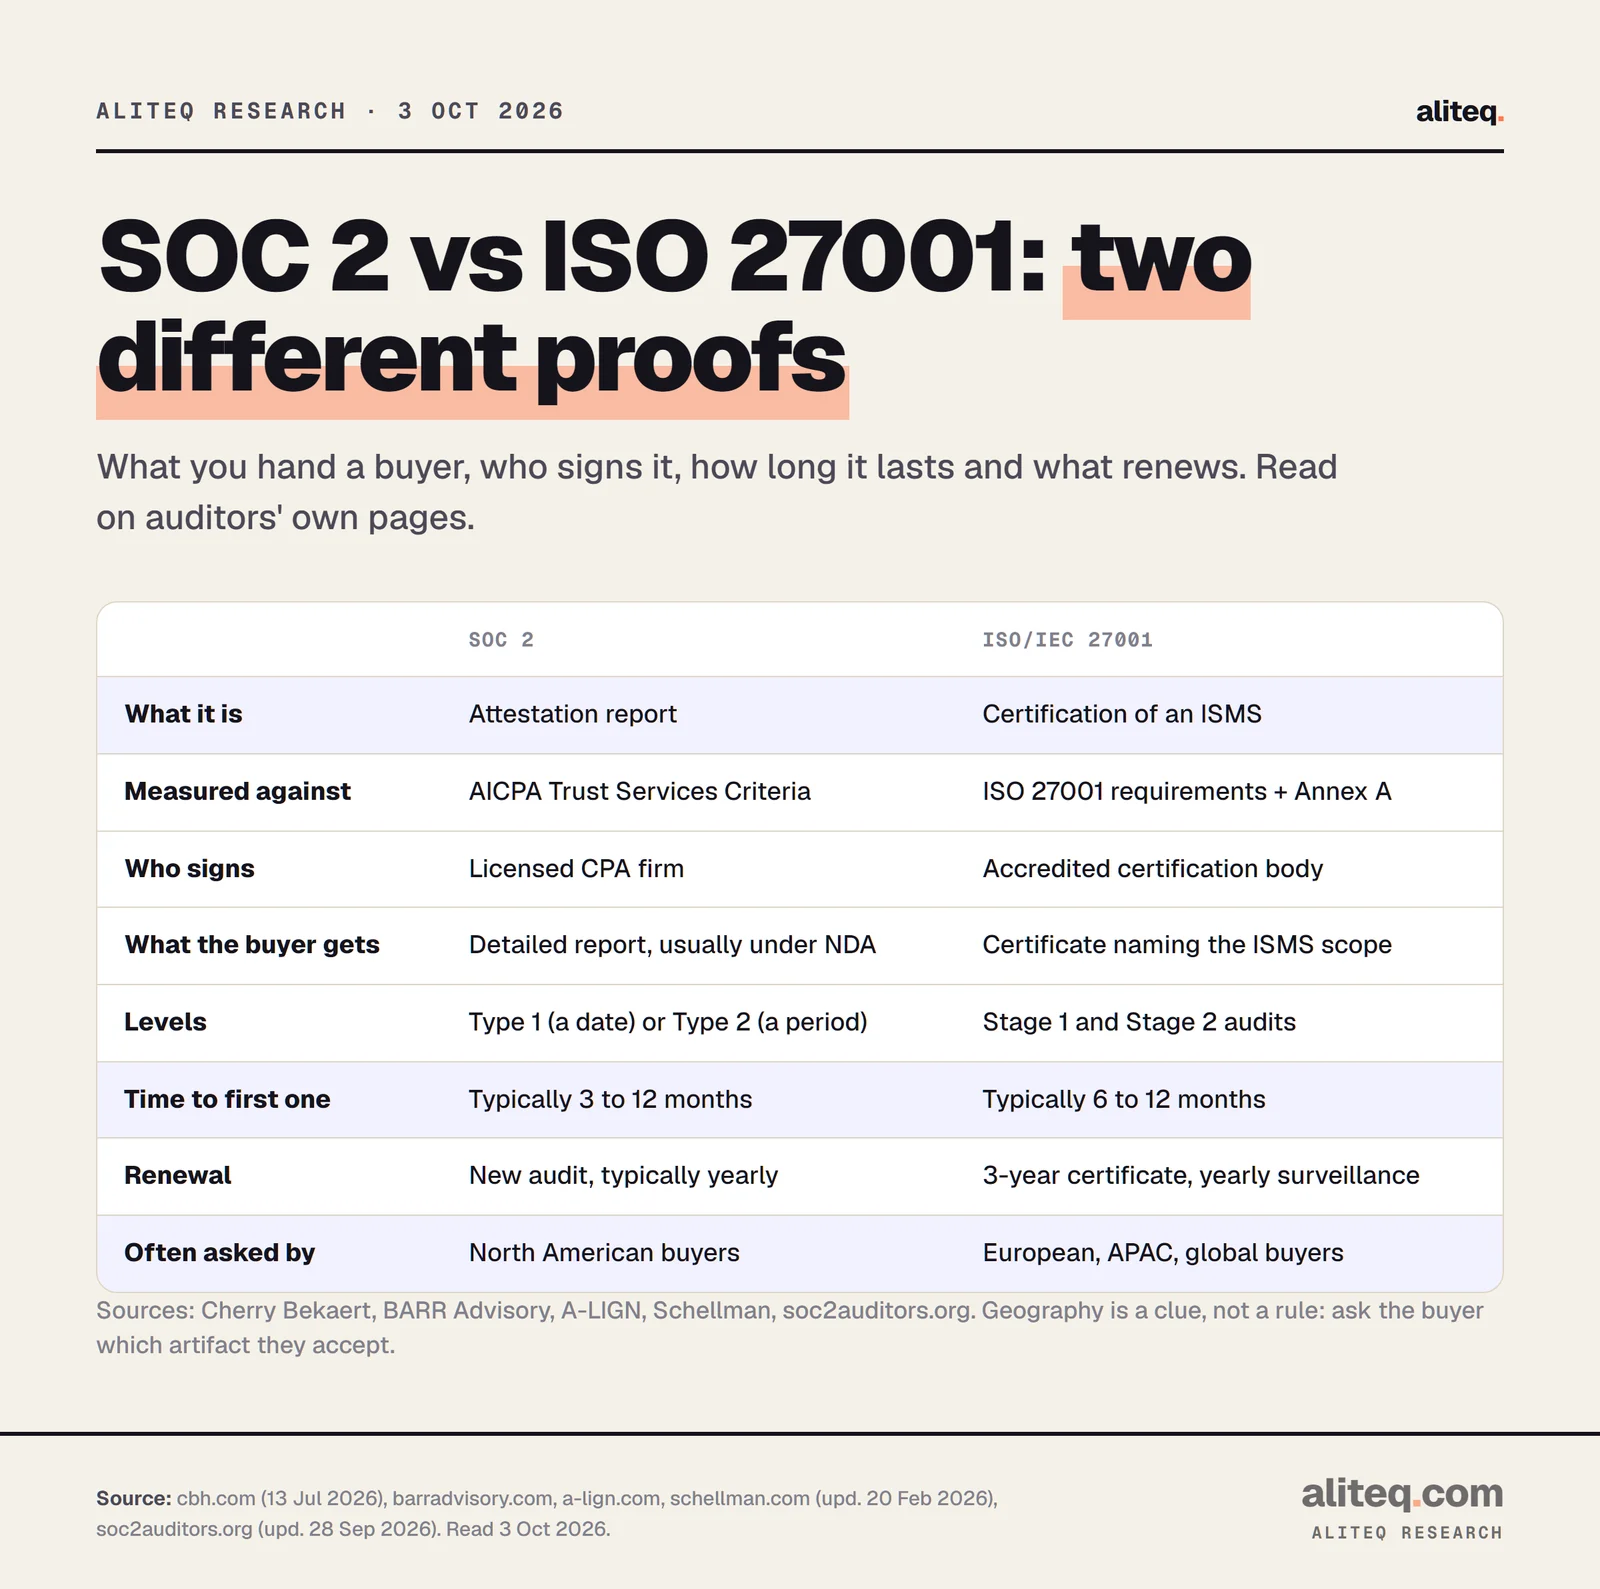
SOC 2 is a report from a licensed CPA firm on your controls. ISO 27001 is a certificate from an accredited certification body that your information security management system (ISMS) meets the standard. Different signer, different paper, different renewal.
Read on auditors' and certification bodies' pages, 3 Oct 2026. Geography is a clue, not a rule. · aliteq research
SOC2Auditors.org, an ad-supported directory, puts it this way: SOC 2 "is a CPA firm's opinion on management's description of a service organization's system and its controls against the AICPA Trust Services Criteria." A Type 1 report "addresses control design at a point in time; Type 2 also addresses operation over the stated period." It is "a detailed report for its intended users, rather than a public certificate."
ISO/IEC 27001 "sets requirements for an information security management system (ISMS). An accredited certification body can certify the defined ISMS scope." The same page warns that the certificate "is not proof that every product, office, or supplier is covered," so check the scope line on any certificate you receive.
A few more differences from the CPA firm Cherry Bekaert (13 Jul 2026) and BARR Advisory:
Name. BARR notes SOC 2 "results in an attestation report rather than certification, so your organization would use the term 'SOC 2 compliance,' not certification."
Scope. SOC 2 is scoped to specific systems or services, and Security is the only mandatory criterion. ISO 27001 covers the ISMS you define. BARR counts "93 Annex A control recommendations."
Internal audit. Cherry Bekaert says SOC 2 does not require one; ISO 27001 requires it under clause 9.2.
Visibility. SOC 2 reports are typically shared under confidentiality agreements. An ISO certificate is generally public, valid for three years, with surveillance audits (Cherry Bekaert, Drata).
Type 1 and Type 2. A-LIGN calls Type 1 "a point-in-time snapshot that validates your controls are suitably designed and in place" and Type 2 proof they are "operating effectively over time – typically a 3 to 12 month period."
Who asks for SOC 2 and who asks for ISO 27001?
Auditors and certification bodies say US and North American buyers more often ask for SOC 2, and European, Asia-Pacific and other international buyers more often ask for ISO 27001. None of these pages is a survey. Treat it as a pattern, and confirm in the buyer's own words.
Schellman (a CPA firm and accredited certification body, updated 20 Feb 2026): "SOC 2 can be particularly important for clients in the United States, ISO 27001 is recognized globally and is often required by clients in Europe, Asia, and other international markets."
Cherry Bekaert (13 Jul 2026): "SOC 2 is often requested by North American customers, while ISO 27001 is recognized globally." It adds that many North American organizations ask for SOC 2 reports "as part of their third-party vendor management due diligence," and that both are "recognized globally."
BARR Advisory (2023): SOC 2 "is more common for organizations based in the U.S. or with U.S.-based customers." Its customer example added ISO 27001 after SOC 2 because it is "more widely recognized internationally—especially in Europe."
Drata, a compliance software vendor: "US-based customers frequently require SOC 2, while international clients often expect ISO 27001 certification."
The directory SOC2Auditors.org adds the caveat that matters most for a startup: "Geography is a useful clue to what a buyer may recognize, but it cannot override a written procurement requirement. A US customer can request ISO 27001, and an EU customer can request SOC 2." It also says the two do not substitute for each other "unless the buyer explicitly accepts the other artifact."
On law: neither is legally required for most companies (Cherry Bekaert). The same directory says no blanket rule makes ISO 27001 mandatory for suppliers to entities covered by the EU's NIS2 directive: national rules and the customer contract decide. That is the directory's reading, not a legal opinion, so check the rules that apply to you. For what to do when a buyer's request lands, see an enterprise customer asked for SOC 2, and for questionnaires that arrive instead of a report, AI security questionnaire answers.
What does each cost?
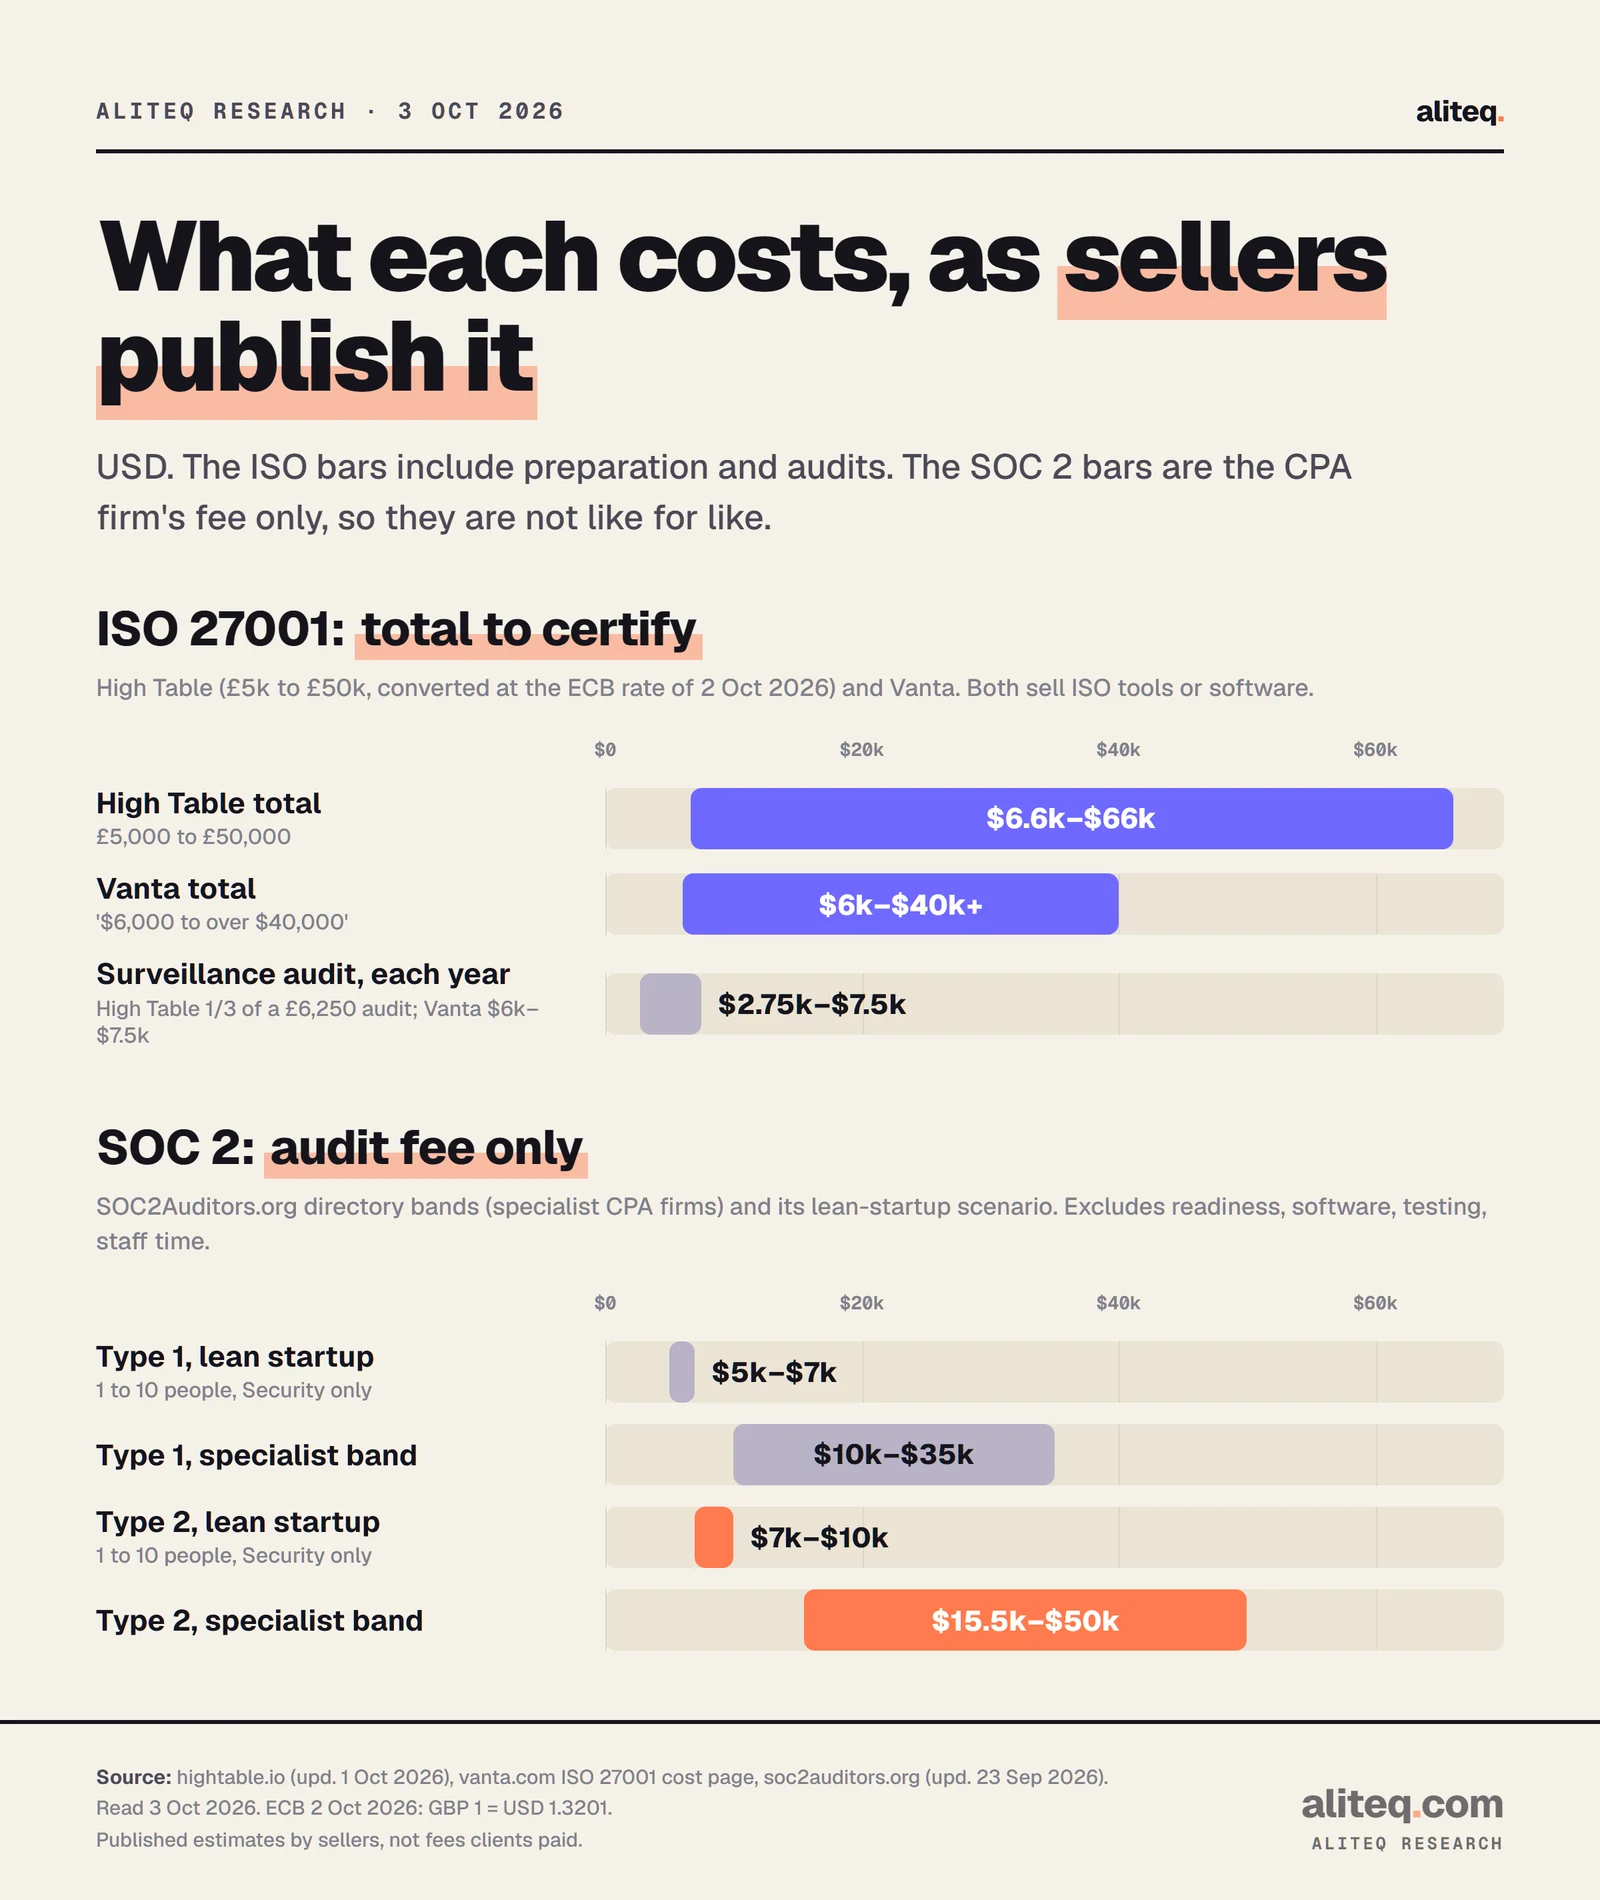
Published ISO 27001 totals run from about $6,600 to $66,000 for the whole path to certification, and a SOC 2 Type 2 audit fee alone runs $7,000 to $10,000 for a lean startup and $15,500 to $50,000 across specialist CPA firms. The two numbers measure different things, so do not subtract one from the other.
Seller-published planning ranges, read 3 Oct 2026. Pounds at the ECB rate of 2 Oct 2026. Not quotes. · aliteq research
ISO 27001, what sellers publish:
High Table (ISO toolkit seller, upd. 1 Oct 2026)
Total
£5,000 to £50,000, about $6,600 to $66,000
Audit parts
Certification audit £3,500 to £15,000; a 1 to 10 person company about £6,250 (about $8,250); "about six months"
Vanta (software vendor)
Total
"$6,000 to over $40,000"
Audit parts
Stage 1 and 2 audits "$14,000-$16,000"; gap analysis $5,000 to $8,000
Secureframe (software vendor)
Total
up to $40,000 preparation
Audit parts
"$15,000+" certification audit; "$10,000 per year" for maintenance and surveillance
Total
Audit parts
High Table (ISO toolkit seller, upd. 1 Oct 2026)
£5,000 to £50,000, about $6,600 to $66,000
Certification audit £3,500 to £15,000; a 1 to 10 person company about £6,250 (about $8,250); "about six months"
Vanta (software vendor)
"$6,000 to over $40,000"
Stage 1 and 2 audits "$14,000-$16,000"; gap analysis $5,000 to $8,000
Secureframe (software vendor)
up to $40,000 preparation
"$15,000+" certification audit; "$10,000 per year" for maintenance and surveillance
After year one you pay surveillance audits in years 1 and 2 and a full recertification in year 3. High Table says surveillance costs "approximately 33% of your initial certification fee" (about $2,750 on a £6,250 audit) and recertification about the same as the first audit. Vanta says surveillance runs "roughly $6,000 to $7,500." The audit fee is one slice. Vanta also lists a pen test ($5,000 to $20,000) and the $350 for the standards documents, and both Vanta and Secureframe put consultants in the $30,000 to $38,000 range. See what a pen test costs for that line.
SOC 2, audit fee only (SOC2Auditors.org, updated 23 Sep 2026): specialist CPA firms list Type 1 at $10,000 to $35,000 and Type 2 at $15,500 to $50,000. Its lean-startup scenario (1 to 10 people, simple SaaS, Security only, controls ready) is $5,000 to $7,000 for Type 1 and $7,000 to $10,000 for Type 2. Those bands exclude readiness, software, testing and staff time. The full breakdown is in what a SOC 2 audit costs, and if you are choosing a compliance platform, see Vanta vs Drata vs Secureframe.
Nobody publishes a price list for the audit itself. These are estimates from sellers with a reason to anchor you, so get two or three written quotes with scope and surveillance included.
How long does each take?
Plan on 3 to 12 months for a SOC 2 and 6 to 12 months for a first ISO 27001, with the clock set mostly by how ready your controls are. Both are ranges from firms that sell the audit.
SOC 2 Type 2: the observation window is "typically a 3 to 12 month period" (A-LIGN). Cherry Bekaert says "the AICPA does not specify a minimum allowable audit period for a SOC 2 Type 2 examination, the shortest testing period typically seen in practice is three months."
ISO 27001: Cherry Bekaert says "usually six to 12 months for initial certification." High Table says "about six months." BARR says Stage 1 "generally takes two to three days" and Stage 2 "within one to two weeks" for most organizations, once you are prepared.
Renewal: SOC 2 needs a new audit typically every year. An ISO certificate lasts three years with annual surveillance audits (A-LIGN, Cherry Bekaert). A-LIGN says recertification starts with a full audit, and organizations "do not typically need to go through the Stage 1 audit again."
A SOC 2 Type 1 is usually the faster document if a buyer will accept it. Ask whether they will, and for how long.
How much do SOC 2 and ISO 27001 overlap?
Quite a lot of the day-to-day work is shared: access control, risk assessment, incident response, change management and vendor management show up in both. Nobody can give you a trustworthy percentage, so plan the overlap by mapping, not by headline.
The AICPA publishes a resource called "Mapping: 2017 Trust Services Criteria to ISO 27001" (dated 4 May 2018, "includes March 2020 updates"). The file is for AICPA and CIMA members only, so I did not read it, and the page does not say which edition of ISO 27001 it maps. Vanta's mapping page says the AICPA's spreadsheet "demonstrates that the vast majority of SOC 2 and ISO controls overlap" but adds "there's no definitive answer" on how much. Drata says "an estimated 40-85% control overlap," a wide range with no method behind it. Its examples, which are a vendor's own: SOC 2's CC6 (logical and physical access) maps to ISO 27001 Annex A.5 and A.8, and CC3.2 (risk assessment) aligns with Clause 6.1.
What does not carry over, per the sources above:
ISO 27001 needs a management system: a defined ISMS scope, a risk treatment process, a Statement of Applicability, and an internal audit (clause 9.2).
SOC 2 needs a system description and, for Type 2, operating evidence across the whole period you pick.
Each audit tests on its own. SOC2Auditors.org: "neither auditor is bound to accept the first auditor's work without its own examination."
If you want it simple: build one set of policies, one risk register, and one evidence folder, then let each auditor sample what they need.
Do you need both?
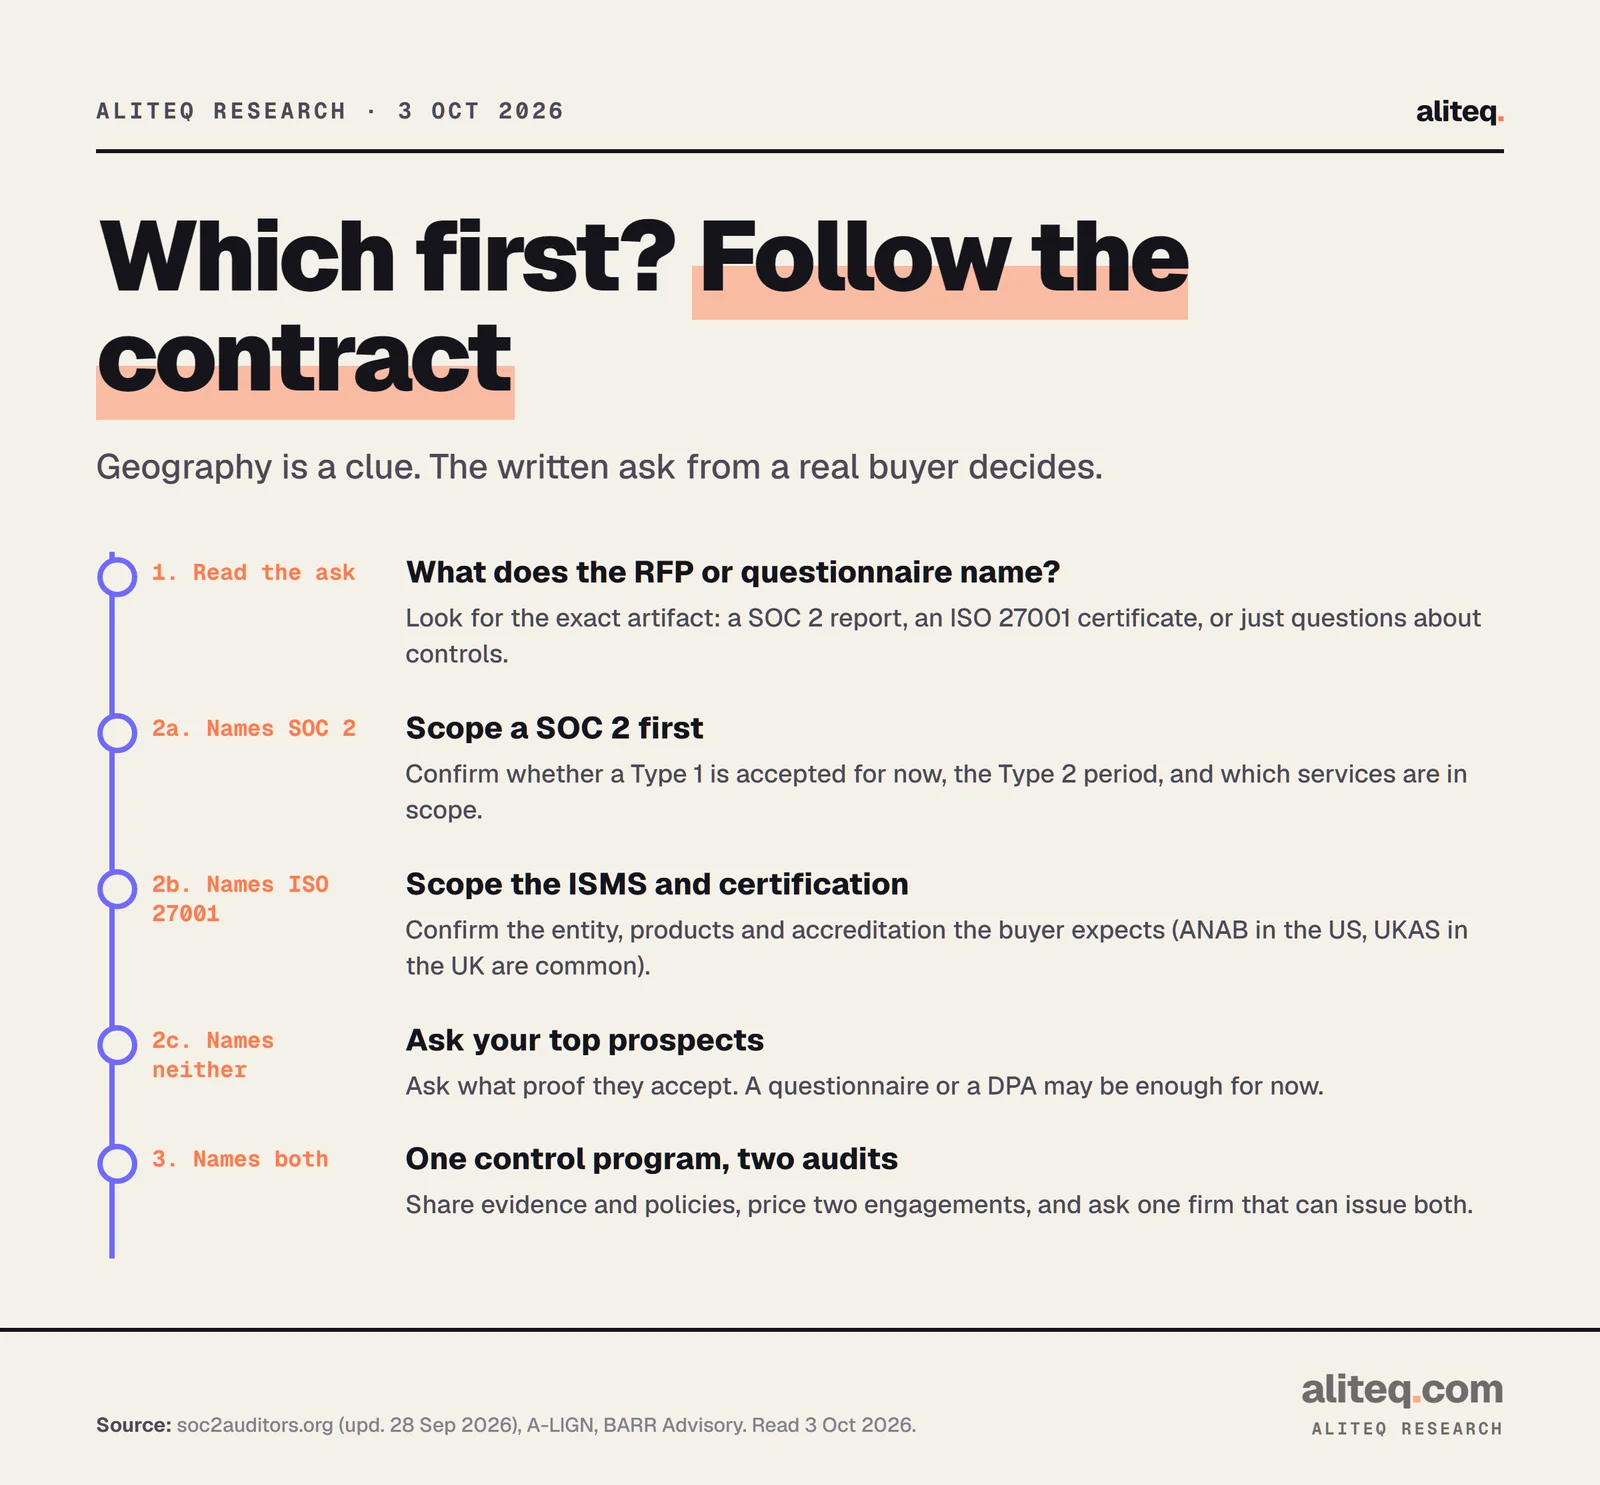
Only when buyers in both camps name both in writing. Otherwise do the one your best-qualified buyer asks for first, and map the second later. A startup selling to US enterprises usually needs SOC 2 first; one selling into Europe or APAC usually needs ISO 27001 first.
A contract-first path, after SOC2Auditors.org's 'which first' guidance. · aliteq research
A US buyer's RFP asks for a SOC 2 Type 2
First move
Scope a SOC 2
Check before you sign
Whether a Type 1 is accepted for now, and the period
A European or UK buyer asks for an ISO 27001 certificate
First move
Scope the ISMS and certification
Check before you sign
Which entity, products and accreditation body they expect
Buyers in both regions name both
First move
One control program, two audits
Check before you sign
Whether one firm can issue both; price both engagements
Nobody has named either
First move
Ask the highest-value prospects what proof they accept
Check before you sign
Whether a questionnaire or a DPA will do for now
You hold SOC 2 and an ISO buyer appears
First move
Map your existing evidence, add the ISMS pieces
Check before you sign
The second auditor's own acceptance of your records
You hold ISO 27001 and a US buyer wants SOC 2
First move
Write the system description, pick a Type 2 period
Check before you sign
Do not assume the certificate satisfies the request
First move
Check before you sign
A US buyer's RFP asks for a SOC 2 Type 2
Scope a SOC 2
Whether a Type 1 is accepted for now, and the period
A European or UK buyer asks for an ISO 27001 certificate
Scope the ISMS and certification
Which entity, products and accreditation body they expect
Buyers in both regions name both
One control program, two audits
Whether one firm can issue both; price both engagements
Nobody has named either
Ask the highest-value prospects what proof they accept
Whether a questionnaire or a DPA will do for now
You hold SOC 2 and an ISO buyer appears
Map your existing evidence, add the ISMS pieces
The second auditor's own acceptance of your records
You hold ISO 27001 and a US buyer wants SOC 2
Write the system description, pick a Type 2 period
Do not assume the certificate satisfies the request
If you do both, ask about a single assessor. Schellman and BARR Advisory are each a CPA firm and an accredited certification body and say they can run both audits. BARR's attest manager calls it "more like one and a half audits," though they are "two completely separate audits." Savings claims are vendors', not facts: Drata says doing both together "can often reduce total audit costs by 30-40%" and High Table says about 30%. SOC2Auditors.org says "no fixed bundle discount or universal implementation timeline follows from the standards themselves," and warns that a low first-year number "can omit surveillance, readiness support, or one of the issuers." Compare quotes on the same scope and period.
One practical detail from A-LIGN: accreditation differs by region. In the US, ANAB is, in its words, "the gold standard," and in the UK and parts of Europe "there's a strong preference towards" UKAS. If a buyer requires an accredited certificate, ask which body they recognize.
Estimate the SOC 2 side
This calculator covers the SOC 2 audit and the lines around it for a startup. Use it for the SOC 2 half of the comparison; the ISO side is in the table above.
SOC 2 cost + timeline estimator
Year one
$34.9k–$102k
Year two and later: roughly 40–70% of year one (vendor-reported).
Time to report
9–15 months
Includes the 6-month window. There is no AICPA minimum; 3 months is the practical floor.
Audit fee
specialist CPA, Type 2
$15.5k–$50k
Compliance platform
Vanta/Drata-class, per year
$12k–$28k
Pen test
basic
$5k–$15k
Readiness assessment
skipped
—
Stack upgrades
none selected
—
Your team's time
40–150 h × $60/h
$2.4k–$9k
Ranges from SOC2Auditors.org (directory), Vendr (buyer data), Drata, The Pun Group (CPA firm), Fractional CISO, SecureLeap and Cherry Bekaert (CPA firm); stack prices from Supabase, Vercel and Lovable pricing pages. Checked 27 Sep 2026. Most are published by companies that sell audits or compliance software. An estimate, not a quote.
Where do ISO 27701 and ISO 42001 fit for an AI startup?
They are optional add-ons on top of ISO 27001, worth knowing about but not where to start. BARR Advisory lists ISO 27701 as the privacy information management system (PIMS) extension, and ISO 42001 as a framework "designed to help organizations safely and ethically design and manage artificial intelligence (AI) systems."
I did not re-read ISO 42001 prices today, so I print none. If an AI buyer's questionnaire asks about AI governance, start with AI security questionnaire answers and ask what artifact they actually want. For how AI vendors present their own certifications, see SOC 2 for AI startups: cost and timeline.
Quick answers
Is ISO 27001 or SOC 2 better?
Neither is better. Cherry Bekaert says SOC 2 is commonly preferred by customers in North America and ISO 27001 is more widely recognized internationally. The right one is the one your buyer's written request names.
Does ISO 27001 replace SOC 2 for a US buyer?
Not automatically. SOC2Auditors.org says one artifact substitutes for the other only when the buyer explicitly accepts it, and that a US customer can request ISO 27001 just as an EU customer can request SOC 2. Ask the buyer.
Which costs more, SOC 2 or ISO 27001?
The published numbers measure different things. Sellers put ISO 27001 at about $6,600 to $66,000 in total (High Table, converted at the ECB rate of 2 Oct 2026) and $6,000 to $40,000 or more (Vanta), including preparation. SOC2Auditors.org lists SOC 2 Type 2 audit fees alone at $15,500 to $50,000 for specialist firms and $7,000 to $10,000 for a lean startup. Get quotes on one scope.
Can I do SOC 2 and ISO 27001 at the same time?
Yes. Drata says many organizations complete both within 6 to 9 months when pursued together, and Schellman and BARR Advisory both say a single assessor can run both. Those are sellers' claims. They are still two audits, and each auditor tests on its own.
How long does an ISO 27001 certificate last?
Three years, with annual surveillance audits in years one and two and a recertification audit in year three (A-LIGN, High Table). A SOC 2 report covers the period tested, and Cherry Bekaert says a new audit is typically required each year.
Do I need ISO 27001 because of NIS2 or GDPR?
No source we read says so. SOC2Auditors.org says NIS2 sets risk-management and supply-chain duties and "no blanket rule" requires an ISO 27001 certificate from every supplier, and that GDPR Article 32 does not name ISO certification as a universal condition. That is a directory's reading, so check the rules and contract that apply to you.
The cheapest move is the one that follows the contract. Find out what your best buyer's procurement team will accept, scope that one first, and build the control program so the second audit is mostly sampling. The rest of the compliance map is on the Security & Compliance hub.
Use this in your own page
Teaching this? Paste the live version into your course, blog or answer. Free, no sign-up; the credit line links back here.