a Gitea admin's hosting bill flagged 70% CPU usage. that's how he found the hackers
A bug that lets anyone with a free account plant a git hook is now CISA's problem — and it started with a cryptominer, not a headline.
Aliteq Team · Aug 26 · 6 min
13 articles · newest first

A bug that lets anyone with a free account plant a git hook is now CISA's problem — and it started with a cryptominer, not a headline.
Aliteq Team · Aug 26 · 6 min

CVE-2026-8037 lets anyone run root commands on Kemp LoadMaster appliances with zero credentials — and 792 attack attempts from 65 IP addresses landed before it made the federal watch list.
Aliteq Team · Aug 23 · 6 min

CVE-2026-20349 doesn't steal your data. It just reboots your VPN gateway on command, and Cisco's already watching it happen in the wild.
Aliteq Team · Aug 23 · 6 min

CERT Polska is warning that attackers are actively exploiting an unauthenticated command-injection bug in Zimbra's SNMP monitoring component — one Zimbra quietly fixed five weeks ago, in version 10.1.20.
Aliteq Team · Aug 22 · 6 min

The flaw needs zero login to trigger — just a malicious webpage and a DNS trick — and it's already turning GPU clusters into crypto miners.
Aliteq Team · Aug 20 · 7 min

A Chinese hacker wired DeepSeek into an autonomous attack framework and pointed it at unpatched Apache Tomcat servers, and CISA wants federal systems fixed by Friday — everyone else should move just as fast.
Aliteq Team · Aug 6 · 7 min

CVE-2026-9198 lets anyone run code on a default Langflow install with zero credentials — CISA gave federal agencies two days to patch it.
Aliteq Team · Aug 6 · 6 min

CVE-2026-20316 is a static-credential bug in Secure FMC that's already on CISA's Known Exploited Vulnerabilities list, with a federal patch deadline of August 1.
Aliteq Team · Aug 5 · 6 min

CVE-2026-18577 lets an attacker skip the login screen entirely and pivot straight into every endpoint N-central manages — CISA added it to its must-patch list within 24 hours.
Aliteq Team · Aug 4 · 6 min

CVE-2026-20316 gives anyone the login to a low-privilege account baked into Cisco Secure FMC — and Cisco's own team says it was already being used in the wild before a patch existed.
Aliteq Team · Jul 31 · 7 min

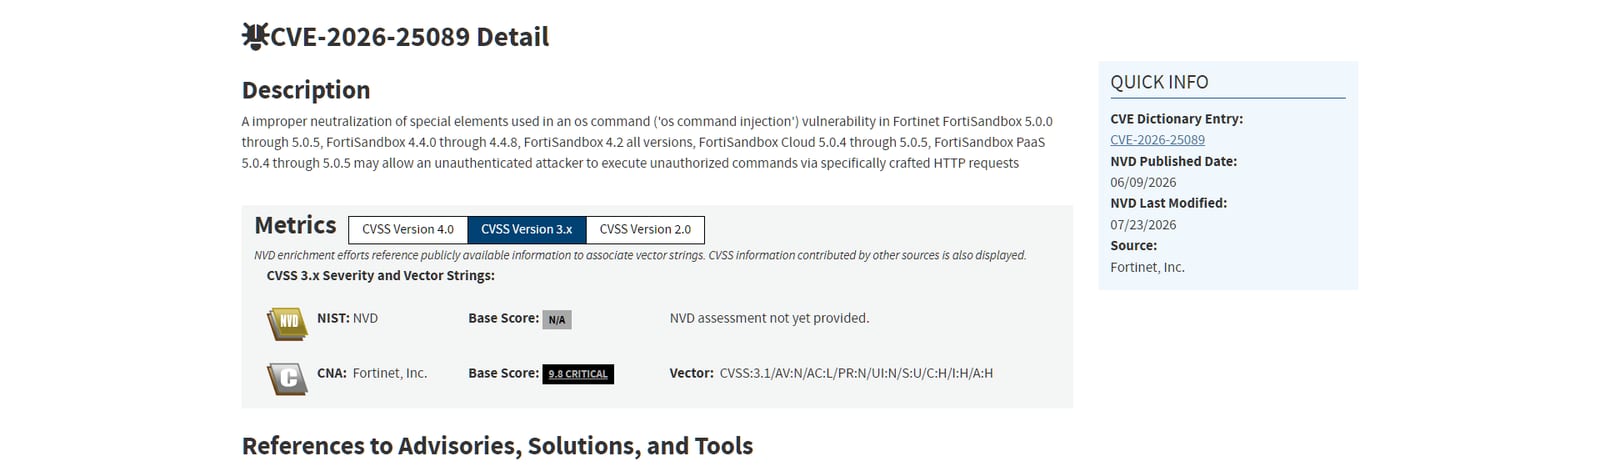
CVE-2026-25089 is an unauthenticated command-injection flaw in FortiSandbox, the security appliance meant to catch malware. It's on CISA's exploited list. The tool that inspects threats has become one.
Aliteq Team · Jul 28 · 9 min

Everyone focused on the SharePoint privilege-escalation zero-day. CVE-2026-58644 is worse: an unauthenticated deserialization flaw that runs code on the server, actively exploited, with a CISA deadline that's already passed.
Aliteq Team · Jul 28 · 9 min

CVE-2026-10520 scores a maximum 10.0 — the rarest severity rating there is. No login, one network request, and an attacker owns the box as root. It's on CISA's exploited list, with public exploit code and confirmed backdoors.
Aliteq Team · Jul 28 · 7 min