An auditor just sent you a quote, or you're about to ask for one. What a SOC 2 audit fee really runs for a company your size, Type 1 against Type 2, boutique against Big Four, what moves the number and what the quote quietly leaves out.
You asked "how much is a SOC 2?" and got a number that could mean four different things. This page answers only one of them: the fee you pay the CPA firm to test your controls and sign the report. Nothing else.
That fee is the one line every quote starts from, and it is also the one line nobody publishes a real price for. No large audit firm we checked posts a price list. What exists instead is a set of published ranges, each from a company that sells something. I read every one I could open on 27 September 2026 and labelled them by who wrote them. If you want the whole first-year budget for a startup, including platform, pen test and timeline, read SOC 2 for AI startups: cost, timeline and what auditors ask instead.
How much does a SOC 2 audit cost?
For a small company, a Type 2 audit fee usually lands between about $15,000 and $50,000 with a specialist firm. A Type 1 lands between about $10,000 and $35,000. Big Four firms charge several times more. The exact figure depends on your scope, not on a price list.
The most-cited bands come from SOC2Auditors.org, an ad-supported directory of audit firms. Its method is worth knowing. Each band runs from the median of the minimum fees its listed firms publish to the median of their maximums. In its own words: "It is not a median of fees clients paid." RedSec Labs, a security firm, splits the market into four tiers and gets wider bands.
SOC 2 audit fee by auditor tier (USD, fee only)
Specialist or boutique CPA firm
Type 1 (SOC2Auditors.org)
$10,000–$35,000
Type 2 (SOC2Auditors.org)
$15,500–$50,000
Type 2 (RedSec Labs)
$15,000–$75,000
Full-service or regional CPA firm
Type 1 (SOC2Auditors.org)
$20,000–$60,000
Type 2 (SOC2Auditors.org)
$30,000–$80,000
Type 2 (RedSec Labs)
$20,000–$95,000
Mid-tier national firm
Type 1 (SOC2Auditors.org)
Not split out
Type 2 (SOC2Auditors.org)
Not split out
Type 2 (RedSec Labs)
$30,000–$120,000
Big Four
Type 1 (SOC2Auditors.org)
$40,000–$145,000
Type 2 (SOC2Auditors.org)
$65,000–$200,000
Type 2 (RedSec Labs)
$60,000–$450,000
Type 1 (SOC2Auditors.org)
Type 2 (SOC2Auditors.org)
Type 2 (RedSec Labs)
Specialist or boutique CPA firm
$10,000–$35,000
$15,500–$50,000
$15,000–$75,000
Full-service or regional CPA firm
$20,000–$60,000
$30,000–$80,000
$20,000–$95,000
Mid-tier national firm
Not split out
Not split out
$30,000–$120,000
Big Four
$40,000–$145,000
$65,000–$200,000
$60,000–$450,000
Linford & Co., a CPA firm that specializes in SOC audits, gives a single anchor. It puts SOC audit costs at $20,000 to $150,000, "with a median price around $30,000". That figure covers SOC 1 and SOC 2 audits of every size, so treat it as a midpoint for the market, not for a startup.
There is no separate certificate fee. SOC 2 is an attestation, a CPA firm's opinion, so the audit fee is the whole external cost of the report itself.
What a SOC 2 audit costs by company size
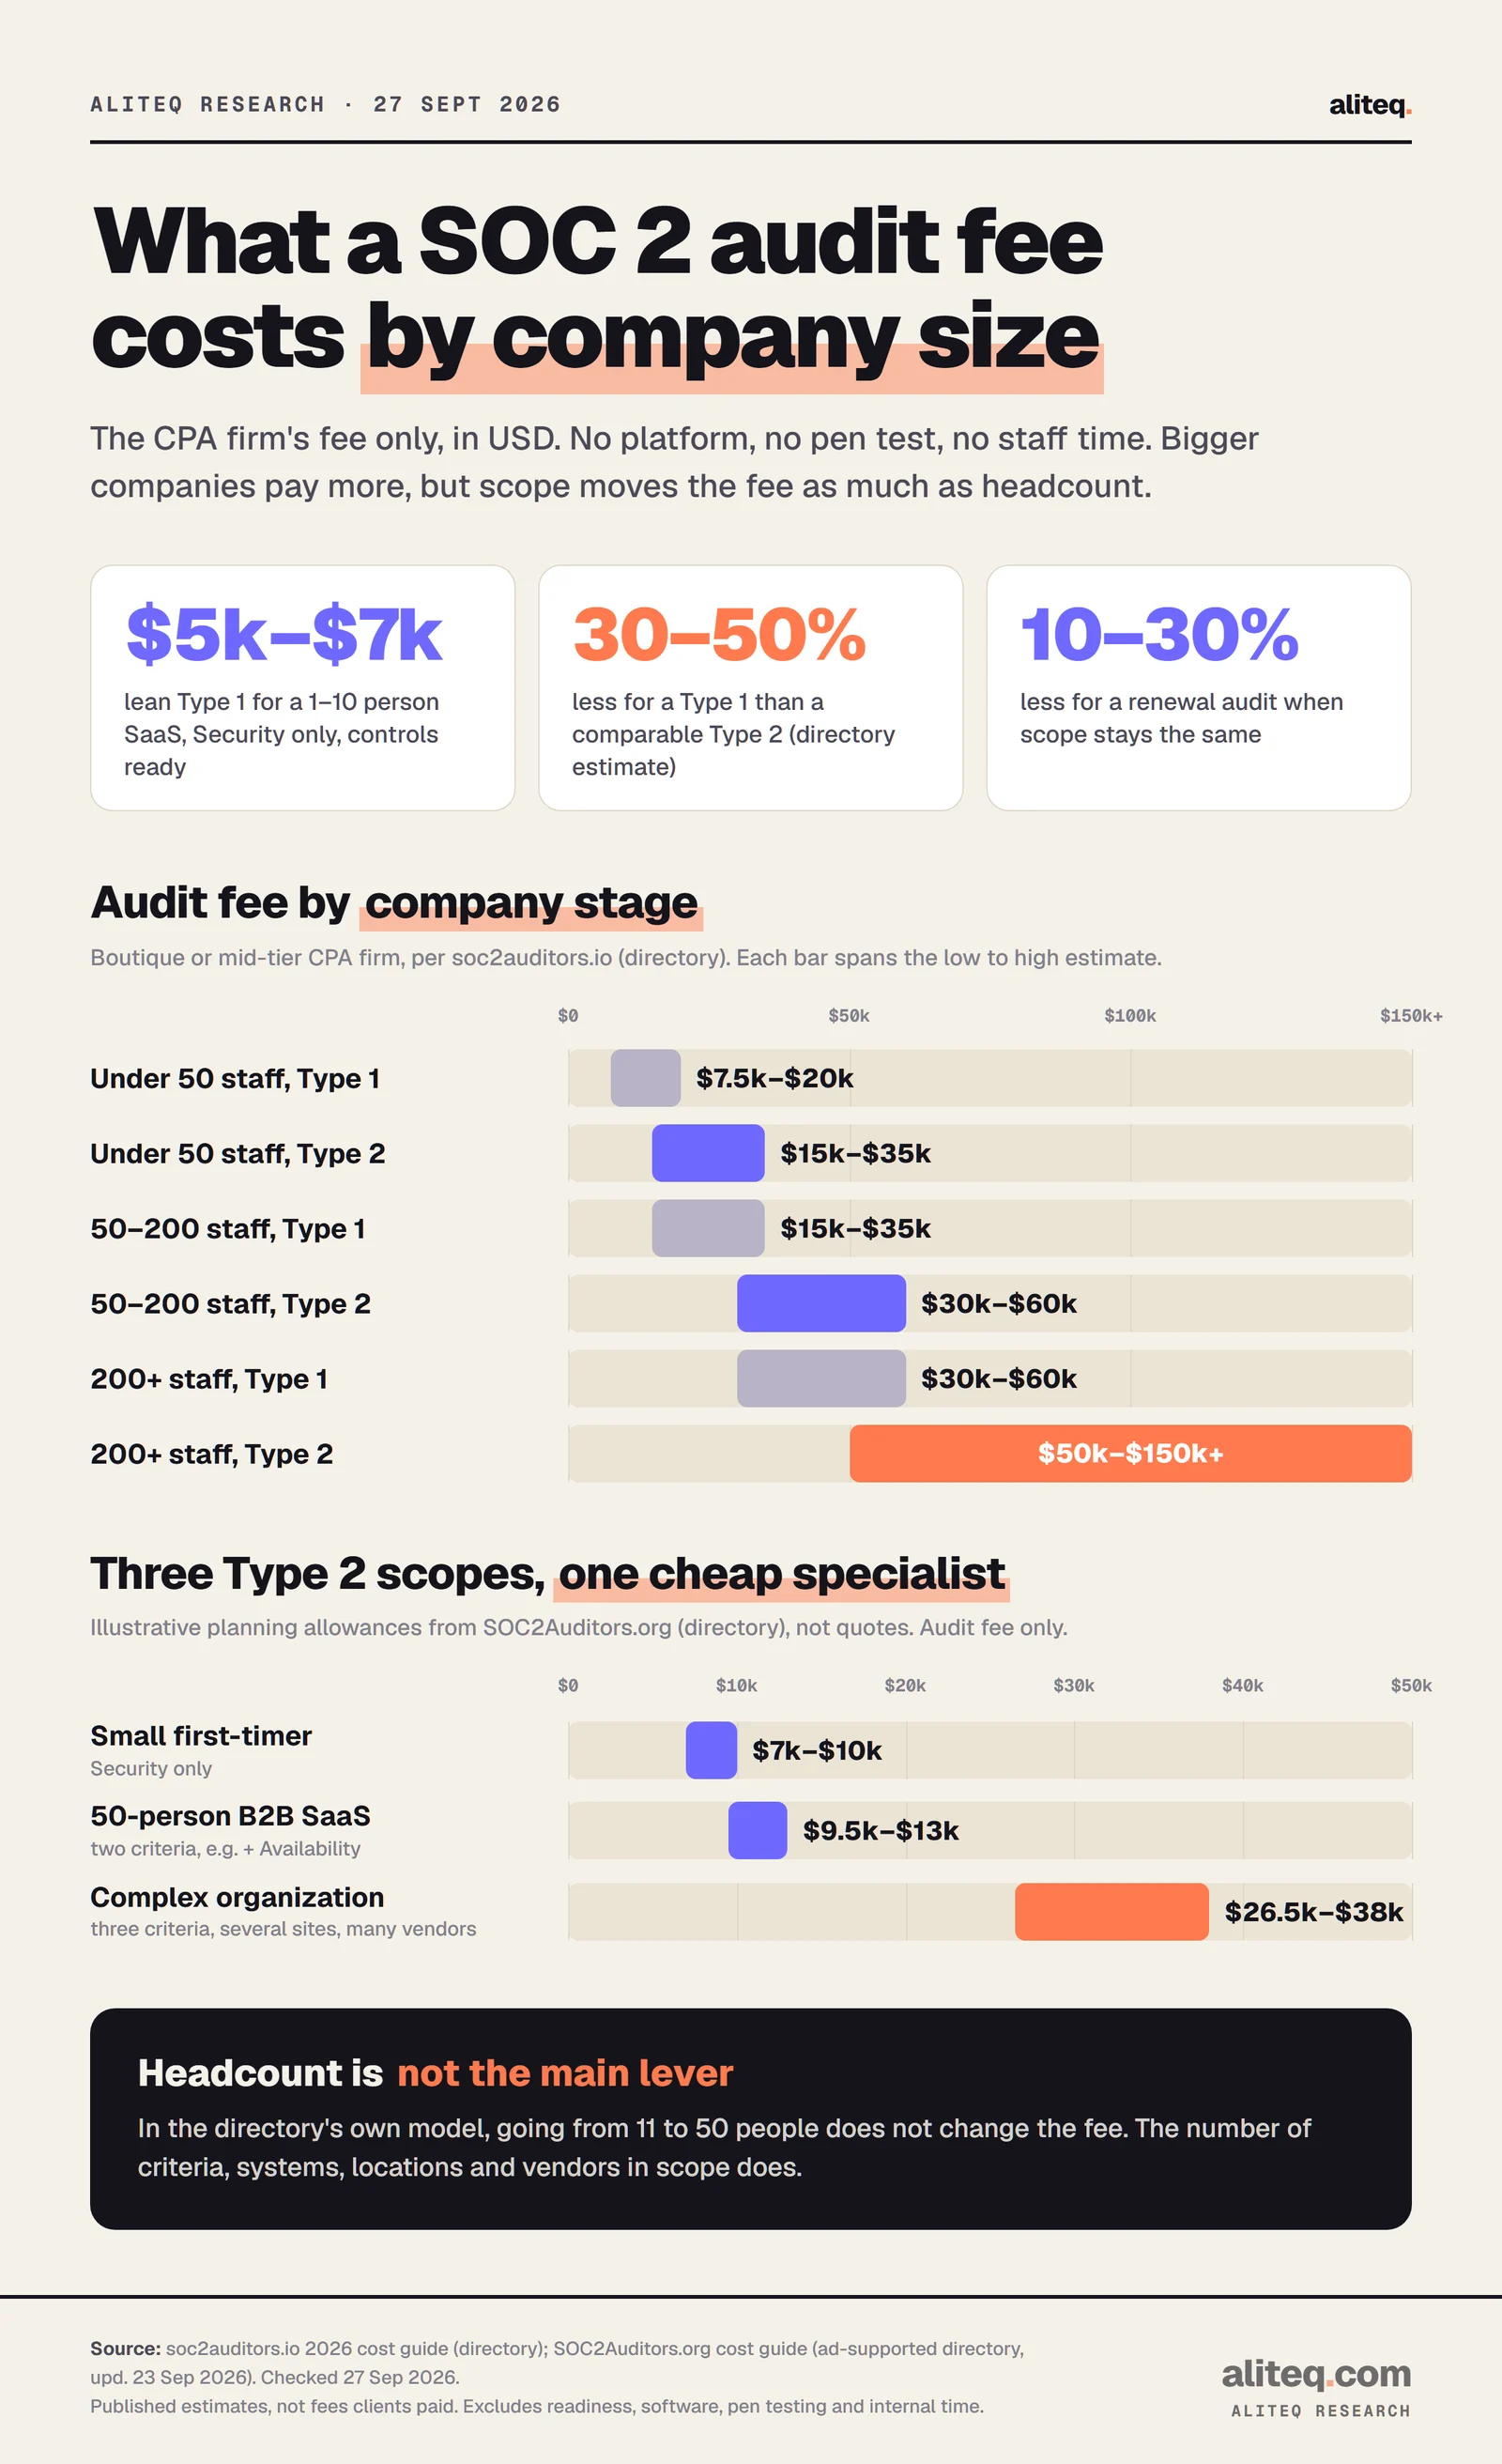
Bigger companies pay more, but not in a straight line. Under 50 people, a Type 2 with a boutique or mid-tier firm runs about $15,000 to $35,000. At 50 to 200 people it runs about $30,000 to $60,000. Past 200 people it starts around $50,000 and can pass $150,000.
Audit fee only. Directory estimates, not fees clients paid. · aliteq research
Those stage bands come from soc2auditors.io, another directory, and assume a boutique or mid-tier auditor. RedSec Labs lands in a similar place from the other side: a Type 2 at $12,000 to $25,000 for a startup or small business, $25,000 to $60,000 mid-market, and $50,000 to $100,000 or more for an enterprise.
The smallest teams can go lower. SOC2Auditors.org suggests a 1–10 person SaaS with a simple system, Security only and controls already in place can shop specialists on a $7,000 to $10,000 Type 2 budget. For a lean Type 1 it uses $5,000 to $7,000.
Here is the detail that surprises people. In that directory's own model, headcount anywhere from 11 to 50 does not change the fee. Its illustrative 50-person SaaS, with two criteria, is budgeted at $9,500 to $13,000. Its "more complex organization," with three criteria, several locations and many vendors, jumps to $26,500 to $38,000. Scope moved the number. People didn't.
Type 1 vs Type 2: the price gap
A Type 1 costs roughly 30 to 50 percent less than a Type 2 of the same scope. It checks your control design on one date. A Type 2 checks the controls worked across a window of months, so the auditor tests more samples over more time.
Two sources agree on that gap from opposite directions. Drata, which sells a compliance platform, says a Type 2 costs 30 to 50 percent more than a Type 1. Soc2auditors.io says a Type I "usually runs 30 to 50 percent less." The Pun Group, a CPA firm, prints a Type I at $5,000 to $20,000 and a Type II at $20,000 to $50,000.
The cheaper report is not always the cheaper choice. If your buyer will only accept a Type 2, a Type 1 is a second audit you pay for on the way. Ask the buyer first. The SOC 2 for AI startups guide covers when a Type 1 is enough and how long each takes.
Why every published range disagrees
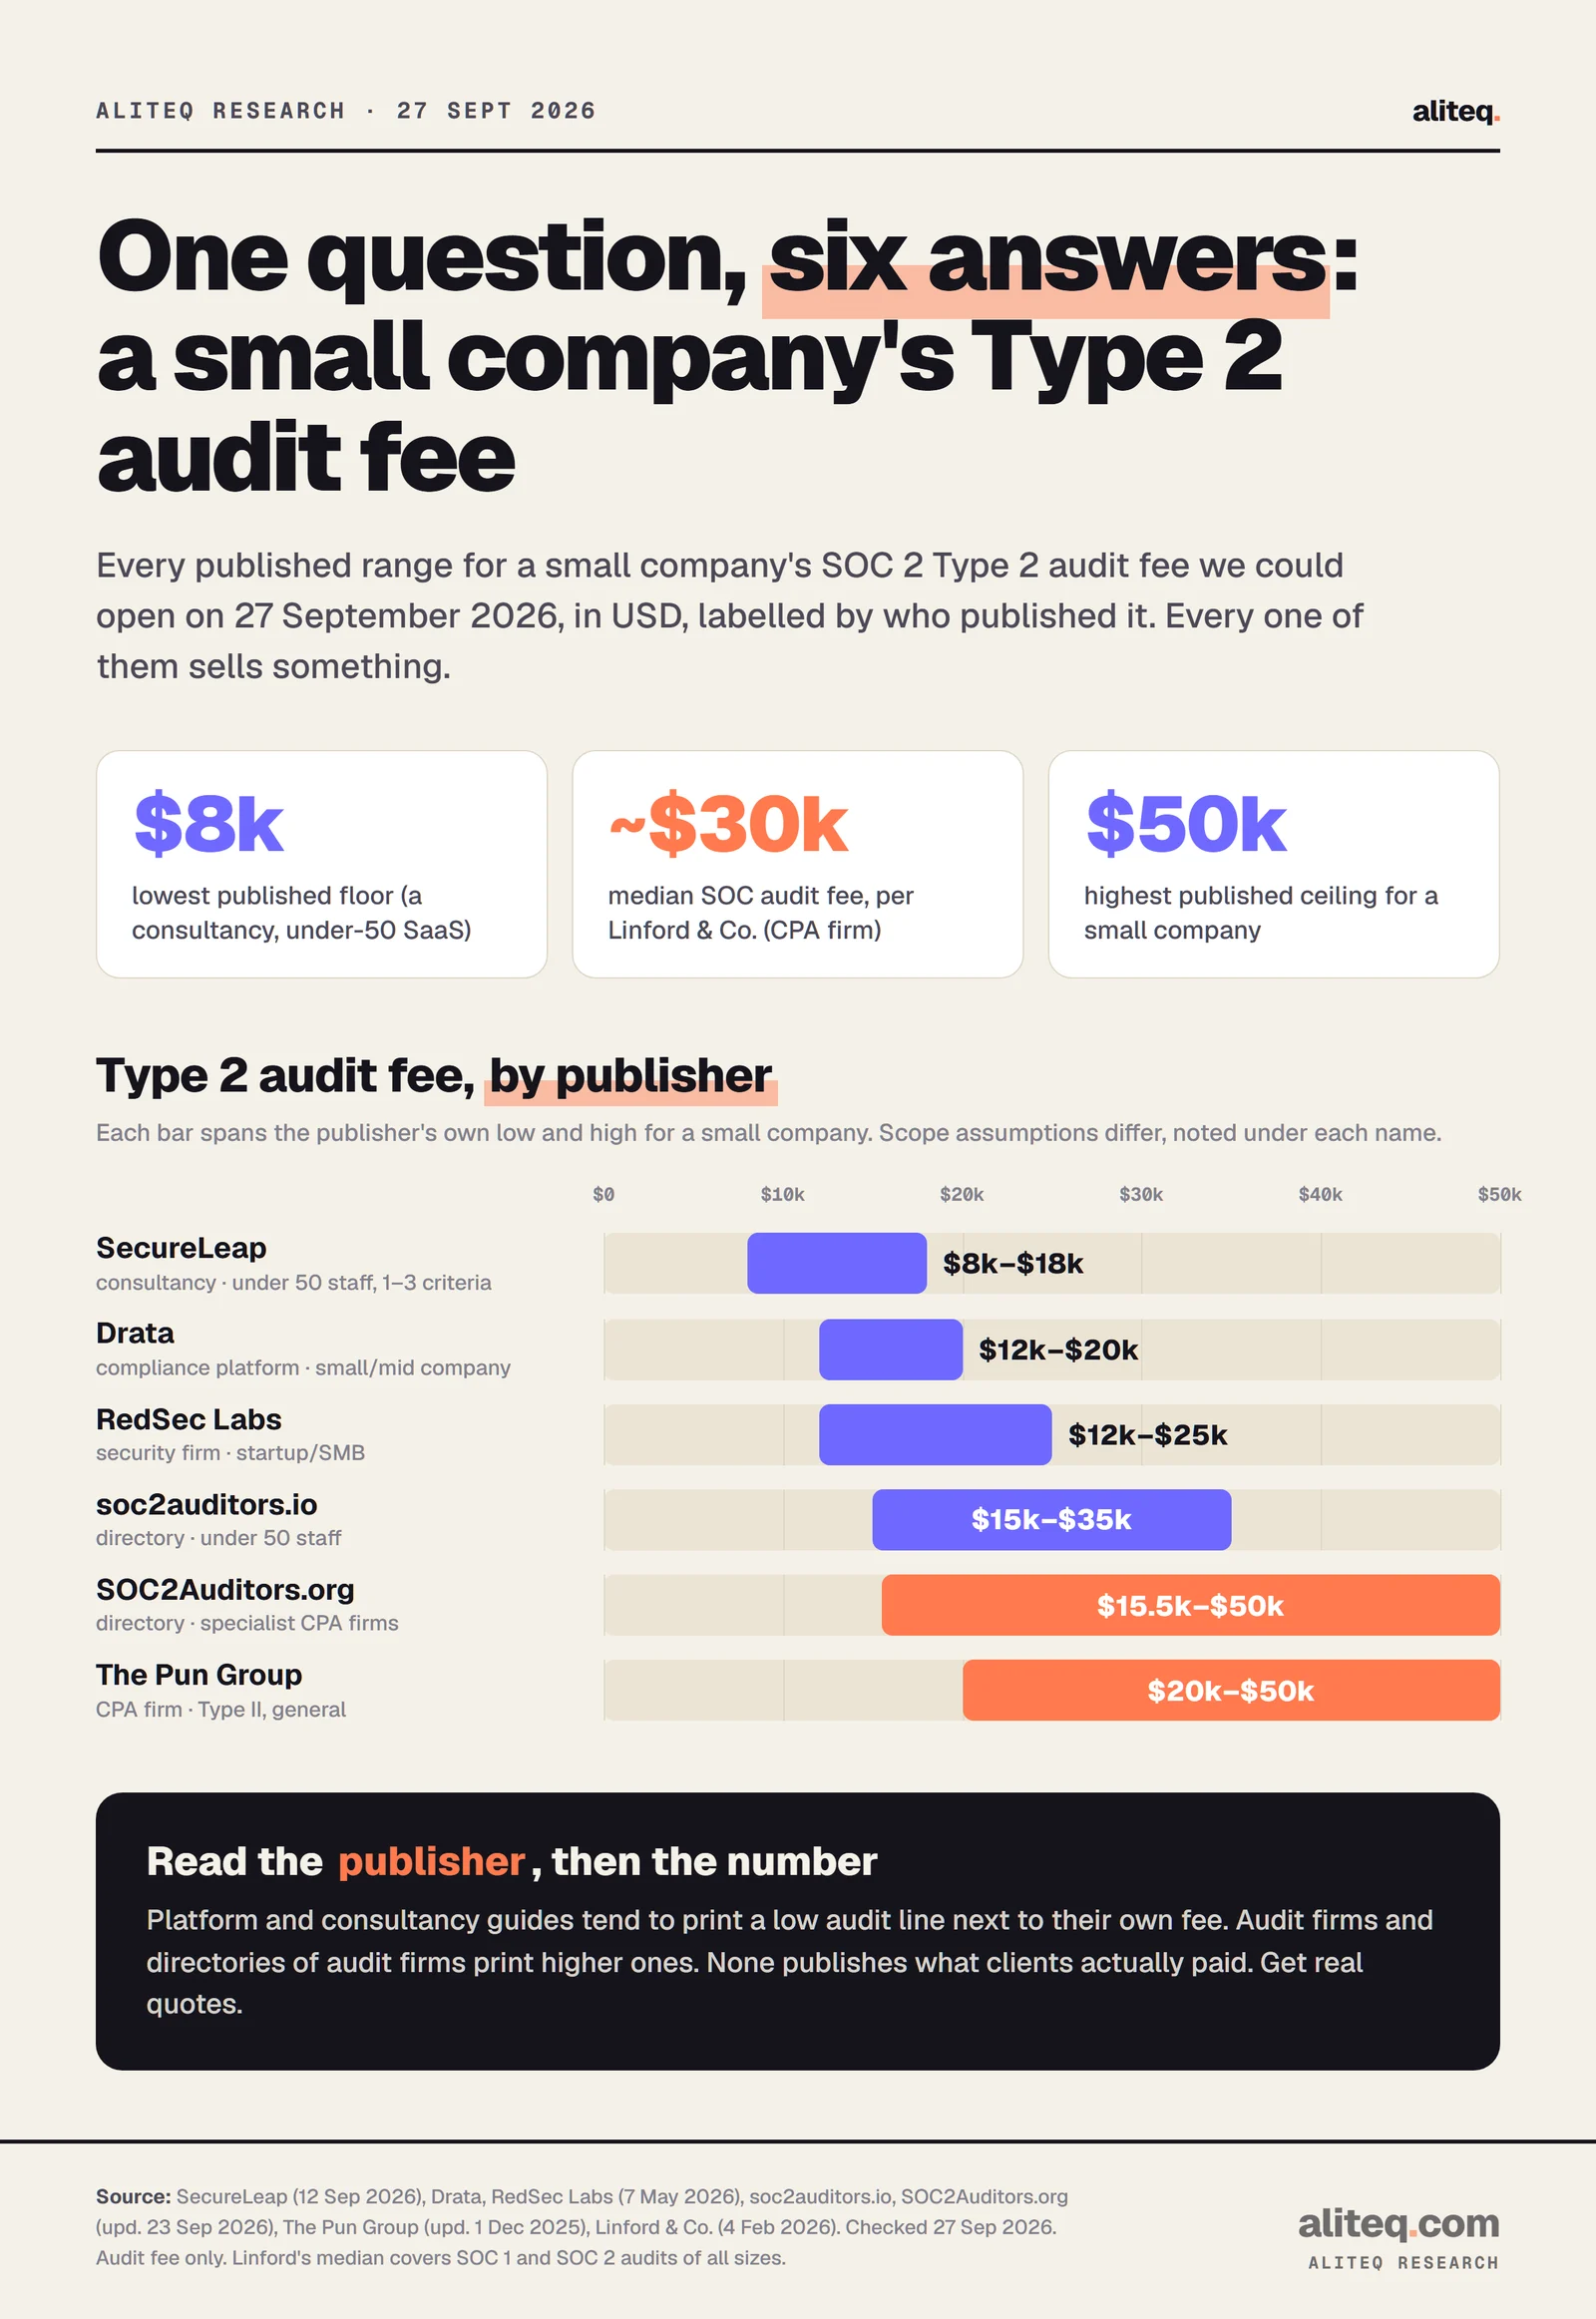
Because each publisher sells something different. Consultancies and platform vendors tend to print a low audit line. Audit firms and directories of audit firms print higher ones. For the same small company, published Type 2 ranges start anywhere from $8,000 to $20,000.
Same question, six published answers. Each publisher's own scope note is under its name. · aliteq research
SOC2Auditors.org names the incentive plainly. It says platform guides put audit figures at $7,500 to $45,000, and that "A platform guide has a reason to keep the audit line small next to its own subscription fee." Vanta, which sells one of those platforms, writes: "The audit fee is the smallest and most predictable part of that number."
Both statements can be true at once. The audit fee often is the smaller line in a first-year budget. It is still the one you sign a contract for, so it is worth pricing properly.
SecureLeap, a consultancy, is the only publisher here that describes its method: ranges drawn from auditor proposals and invoices in its own client work from 2024 to 2026. It puts the Type 2 fee at $8,000 to $18,000 for a SaaS company under 50 people with one to three criteria. That is the low end of the chart, and it is still a seller's sample, not a survey.
What drives a SOC 2 audit quote
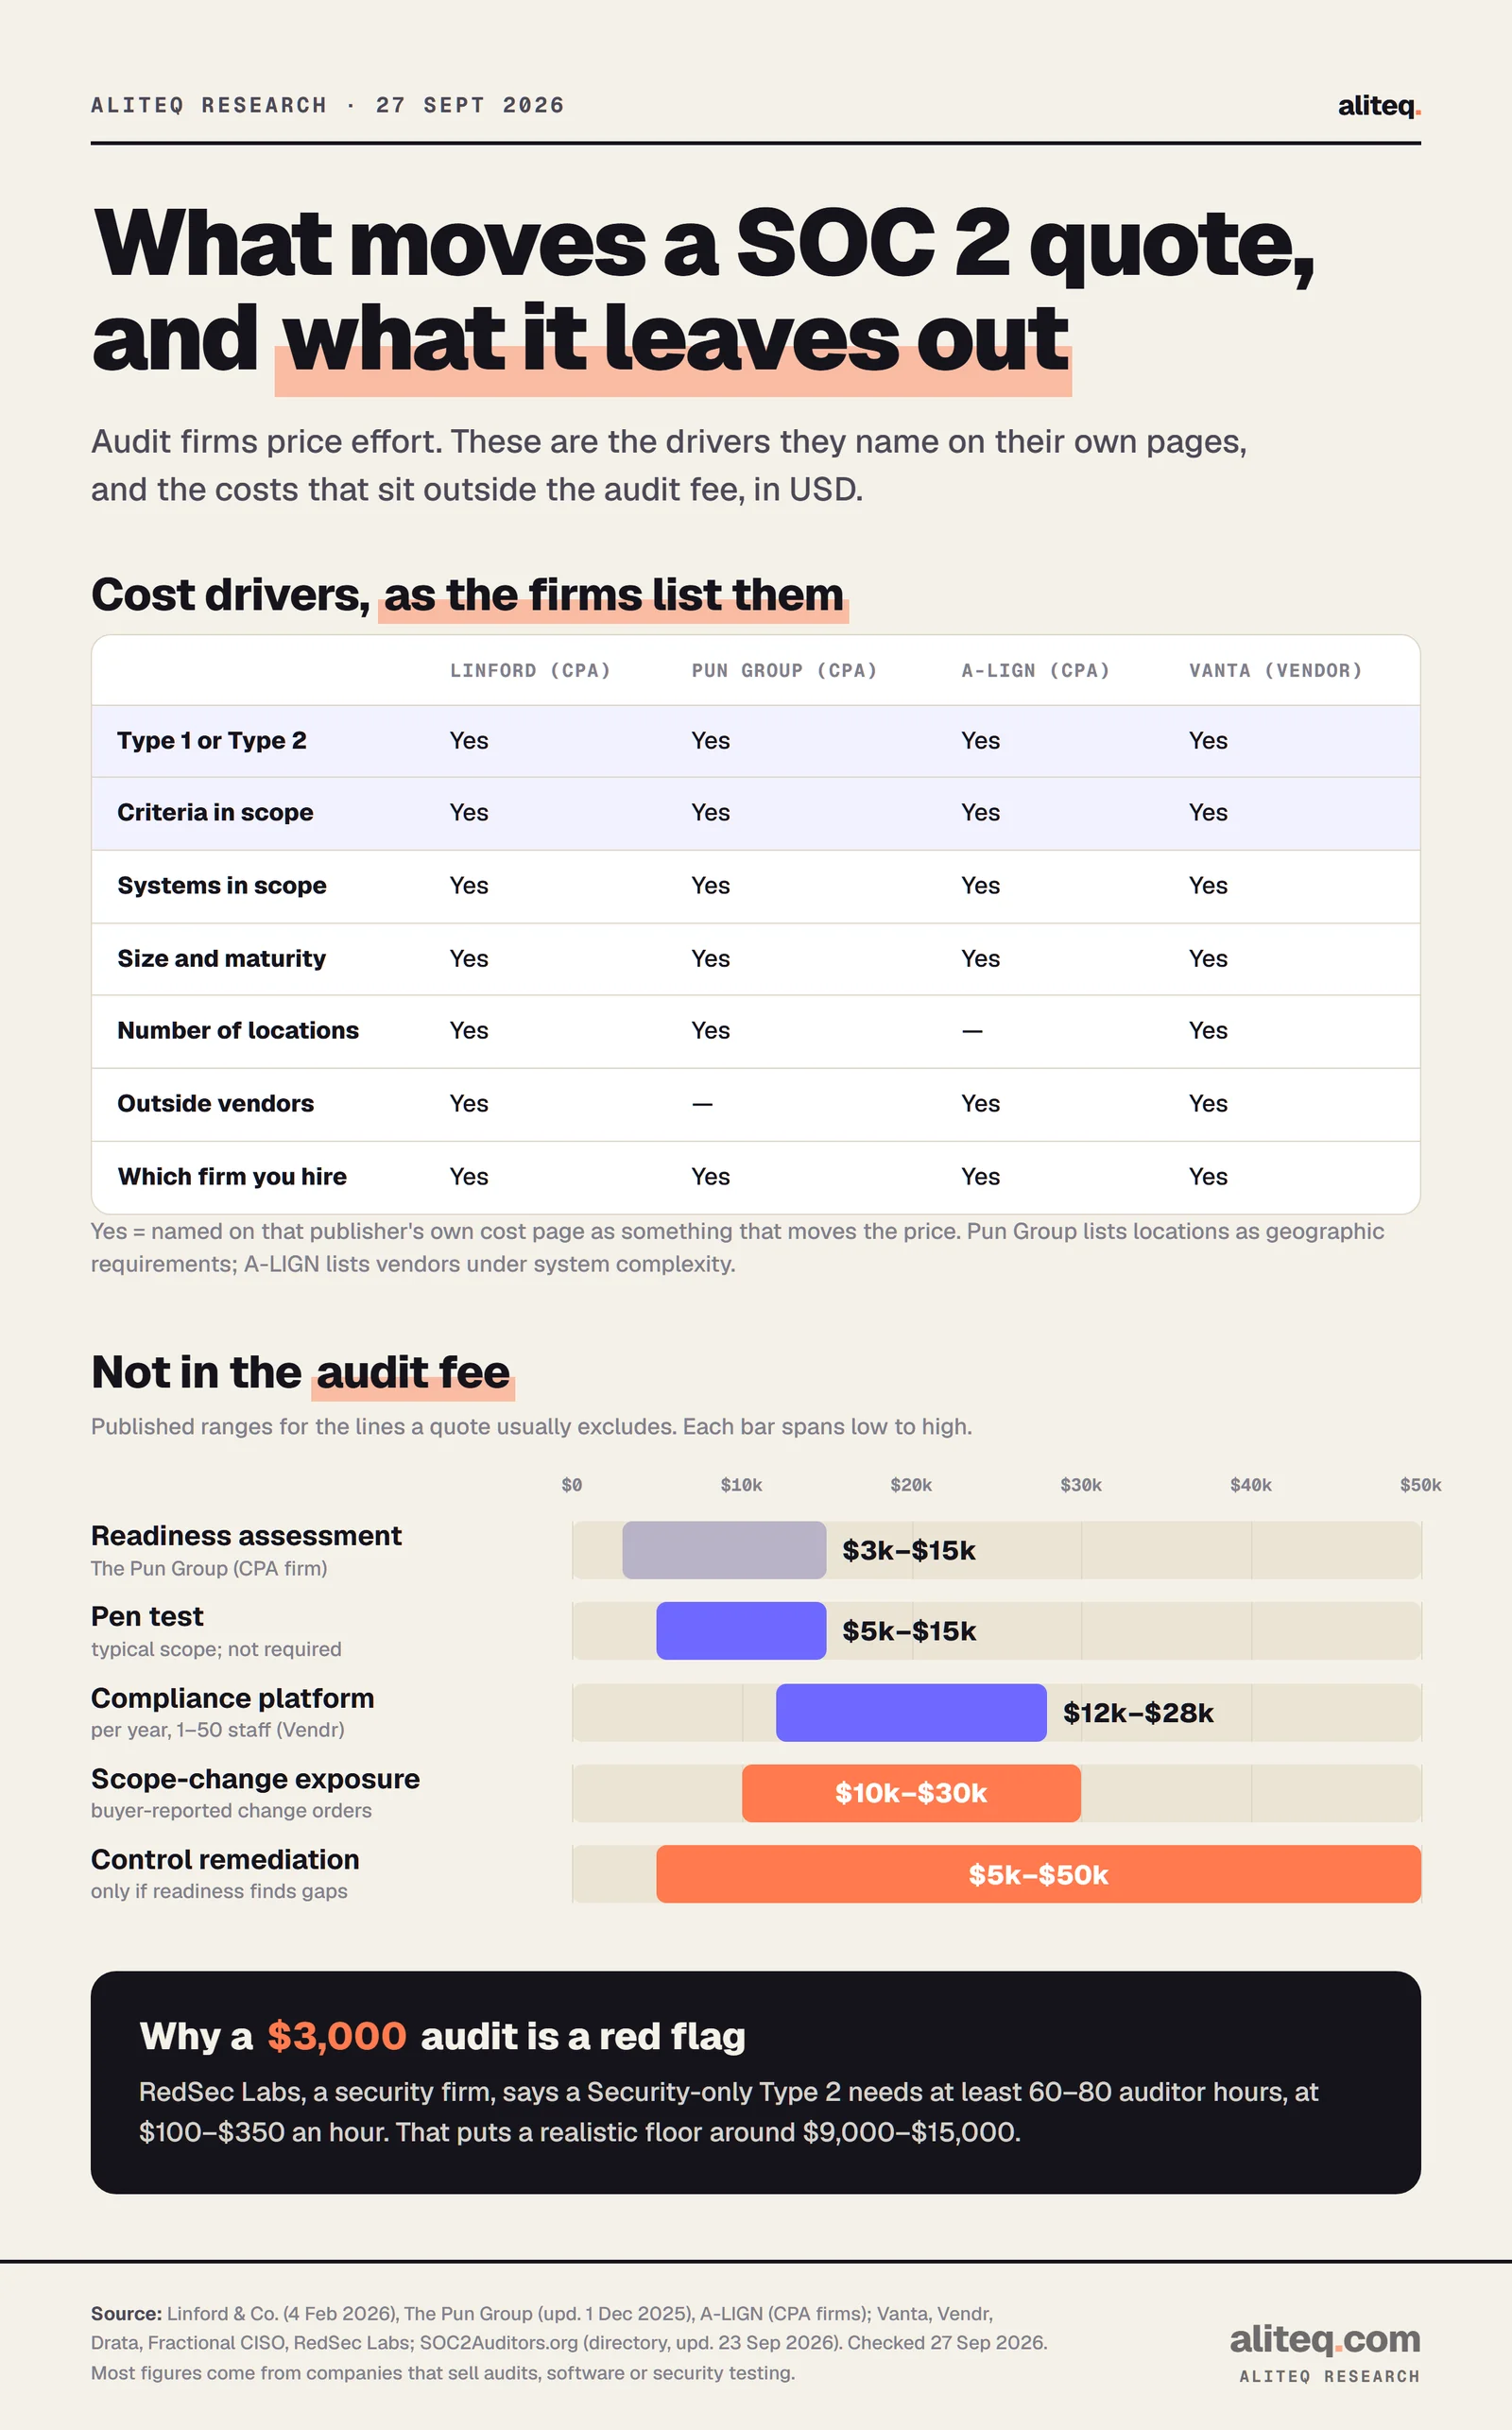
Auditors price effort. Anything that adds hours adds dollars. The firms that describe their pricing name the same short list: report type, which criteria are in scope, how many systems, your size and maturity, your locations, your vendors, and which firm you hire.
Cost drivers as named on the firms' own pages, and the lines a quote usually leaves out. · aliteq research
The drivers, in the order they usually matter for a small company:
Trust Services Criteria in scope. Security is required in every SOC 2. The other four are optional. Linford advises clients to include only Security unless a customer requires more. It says Availability, Processing Integrity and Confidentiality "usually result in smaller incremental increases," while "Adding Privacy is an expensive add-on." Soc2auditors.io estimates each extra criterion commonly adds $5,000 to $15,000.
Systems in scope. Each extra application adds testing. Linford notes the fee "should not double," since only part of the criteria is specific to a technology.
Report type. Type 2 costs more than Type 1, as above.
Size and control maturity. Fewer people means fewer interviews. Undocumented controls mean the auditor spends hours finding them, and you pay for those hours.
Locations. Controls run differently at several sites get tested separately.
Outside vendors. Your cloud host and other subservice providers have to be mapped. Your report usually carves them out, but the auditor still documents how you rely on them.
The firm. Linford, itself a CPA firm, says big firms carry heavy overhead into every fee. A-LIGN lists its own methodology as a cost driver and says it gives "fixed-fee pricing after the scoping session."
Readiness is the lever you control. A mature, documented control set shortens fieldwork. If you are building one from scratch, the six security checks before you share an app cover the access basics an auditor looks at first.
What is not in the SOC 2 audit fee
The audit fee covers the CPA firm's testing and report. It usually excludes readiness work, fixing what readiness finds, a compliance platform, a pen test, your team's hours and next year's audit. Some firms bundle readiness into the fee, so read the quote line by line.
The published ranges for those extra lines:
Readiness assessment: $3,000 to $15,000, per The Pun Group. Linford notes some firms price it separately and some fold it in, so ask for both prices.
Control remediation: $5,000 to $50,000, only when readiness finds work, per SOC2Auditors.org.
Scope-change exposure: $10,000 to $30,000 in buyer-reported change orders, per the same directory. Its advice is to freeze the system boundary and the criteria before fieldwork starts.
Pen test: about $5,000 to $15,000 for a typical scope. SOC 2 does not require one, but most auditors expect some security testing.
Compliance platform: $12,000 to $28,000 a year for 1–50 employees, from buyer data on Vanta. Linford says a platform "can help reduce audit fees," and that "A 10% or 20% fee reduction would be good."
Your team's time. Linford: "Internal costs will often exceed audit fees."
Put the audit fee next to those lines in the calculator below. Pick your firm tier and Type 1 or Type 2 to see the fee on its own, then add the optional lines to see the full first year. Every range in it is sourced; the only number that is yours is what an hour of your team costs.
SOC 2 cost + timeline estimator
Year one
$34.9k–$102k
Year two and later: roughly 40–70% of year one (vendor-reported).
Time to report
9–15 months
Includes the 6-month window. There is no AICPA minimum; 3 months is the practical floor.
Audit fee
specialist CPA, Type 2
$15.5k–$50k
Compliance platform
Vanta/Drata-class, per year
$12k–$28k
Pen test
basic
$5k–$15k
Readiness assessment
skipped
—
Stack upgrades
none selected
—
Your team's time
40–150 h × $60/h
$2.4k–$9k
Ranges from SOC2Auditors.org (directory), Vendr (buyer data), Drata, The Pun Group (CPA firm), Fractional CISO, SecureLeap and Cherry Bekaert (CPA firm); stack prices from Supabase, Vercel and Lovable pricing pages. Checked 27 Sep 2026. Most are published by companies that sell audits or compliance software. An estimate, not a quote.
Red flags in a cheap SOC 2 quote
A very low fee is a warning, not a win. RedSec Labs estimates a Security-only Type 2 needs at least 60 to 80 auditor hours, which puts a realistic floor around $9,000 to $15,000. At $3,000 to $5,000, it says, there are not enough hours to test anything meaningful.
That floor is a security firm's estimate, and it bills auditors at $100 to $175 an hour for staff and $250 to $350 for partners. Treat it as a sanity check, not a rule.
Three warning signs, all from the firms' own pages:
A price with no questions. Linford: "If you get a blind quote (no questions asked), chances are the fees will increase as the audit is performed when 'new facts' are uncovered, or there will be a significant jump in price the following year."
A bundled "partner" auditor at a set low fee. Linford warns about compliance-tool vendors whose partner audit firm quotes "extremely low" fees, and describes a case where auditors gave every client essentially the same form report.
A firm that isn't a licensed CPA firm. Only a licensed CPA firm can issue a SOC 2 report. Linford's summary: "if the report is not completed by a CPA firm, the report should not be relied on."
The AICPA is watching this corner of the market. In May 2026 its Journal of Accountancy quoted Carl Mayes, its vice president for ethics and firm quality: "Some firms are leaning too heavily on third-party SOC platforms without applying the professional judgment required by our standards." Peer reviewers were told to look for identical reports, risk assessments, sample sizes and testing. The AICPA's SOC page also says it is looking into anonymous allegations about a compliance vendor's SOC business. It does not name the vendor. For the Delve allegations TechCrunch reported in March 2026, see the pillar guide.
How to get a SOC 2 quote you can compare
Write your scope down before you ask anyone for a price. Then ask at least two firms from different tiers the same questions, and make them answer in writing. Vanta's checklist is a good minimum: which criteria and systems are in scope, whether readiness, pen testing and remediation are inside the number, and what next year's fee looks like.
Ask your buyer what they need: Type 1, Type 2, which criteria, and by when. Most only need Security.
Freeze your scope: the systems, the criteria and the locations. Scope changes mid-audit are where fees grow.
Send two or three firms the same written scope. A firm that prices without asking questions is a warning sign.
Get line items: audit fee, readiness, pen test, remediation support and expenses, each priced separately.
Check the firm is a licensed CPA firm and ask for its most recent peer review result before you sign.
Ask for next year's fee in writing. SOC 2 is a new audit every year, so the renewal price matters as much as the first.
What the audit costs in year two
You pay for a fresh audit every year. Vanta puts it simply: "The audit itself never goes away." Renewals tend to cost less when scope stays the same, because the auditor already knows your system.
Soc2auditors.io says renewals "often cost 10 to 30 percent less if scope stays stable." Probo, a platform vendor, puts the renewal audit at 70 to 90 percent of the first one, which is the same range said the other way round. Adding a criterion or a system in year two resets that math.
Quick answers
How much does a SOC 2 audit cost?
For a small company, the audit fee alone usually runs about $15,000 to $35,000 for a Type 2 with a boutique or mid-tier CPA firm, and about $7,500 to $20,000 for a Type 1, by directory estimates. Big Four firms start around $60,000 to $65,000 for a Type 2. These are published estimates, not quotes.
How much does a SOC 2 Type 2 audit cost?
Specialist firms run about $15,500 to $50,000, full-service firms about $30,000 to $80,000 and the Big Four about $65,000 to $200,000, per SOC2Auditors.org's directory bands. A 1–10 person team with a simple system may budget $7,000 to $10,000.
Is SOC 2 Type 1 cheaper than Type 2?
Yes, usually by about 30 to 50 percent for the same scope, because a Type 1 checks control design on one date instead of testing over months. If your buyer needs a Type 2, a Type 1 first is an extra audit, so ask before you buy one.
Why do SOC 2 audit quotes vary so much?
Auditors price effort. The number of criteria, systems, locations and vendors in scope, your control maturity and the firm's overhead all change the hours. Publishers of price ranges also sell different things, which shifts where their ranges sit.
What is not included in a SOC 2 audit fee?
Usually readiness work, remediation, a compliance platform, a pen test, your team's time and next year's audit. Some firms bundle readiness in, so ask for each line priced separately.
Do I pay for SOC 2 every year?
Yes. Each report covers a set period, so customers expect a current one and you pay for a new audit each year. Renewals often cost 10 to 30 percent less if the scope stays the same.
The audit fee is one line. For the rest of the first year, the timeline and what your vendors already cover, read SOC 2 for AI startups. Everything else on compliance is on the Security & Compliance hub.
Use this in your own page
Teaching this? Paste the live version into your course, blog or answer. Free, no sign-up; the credit line links back here.