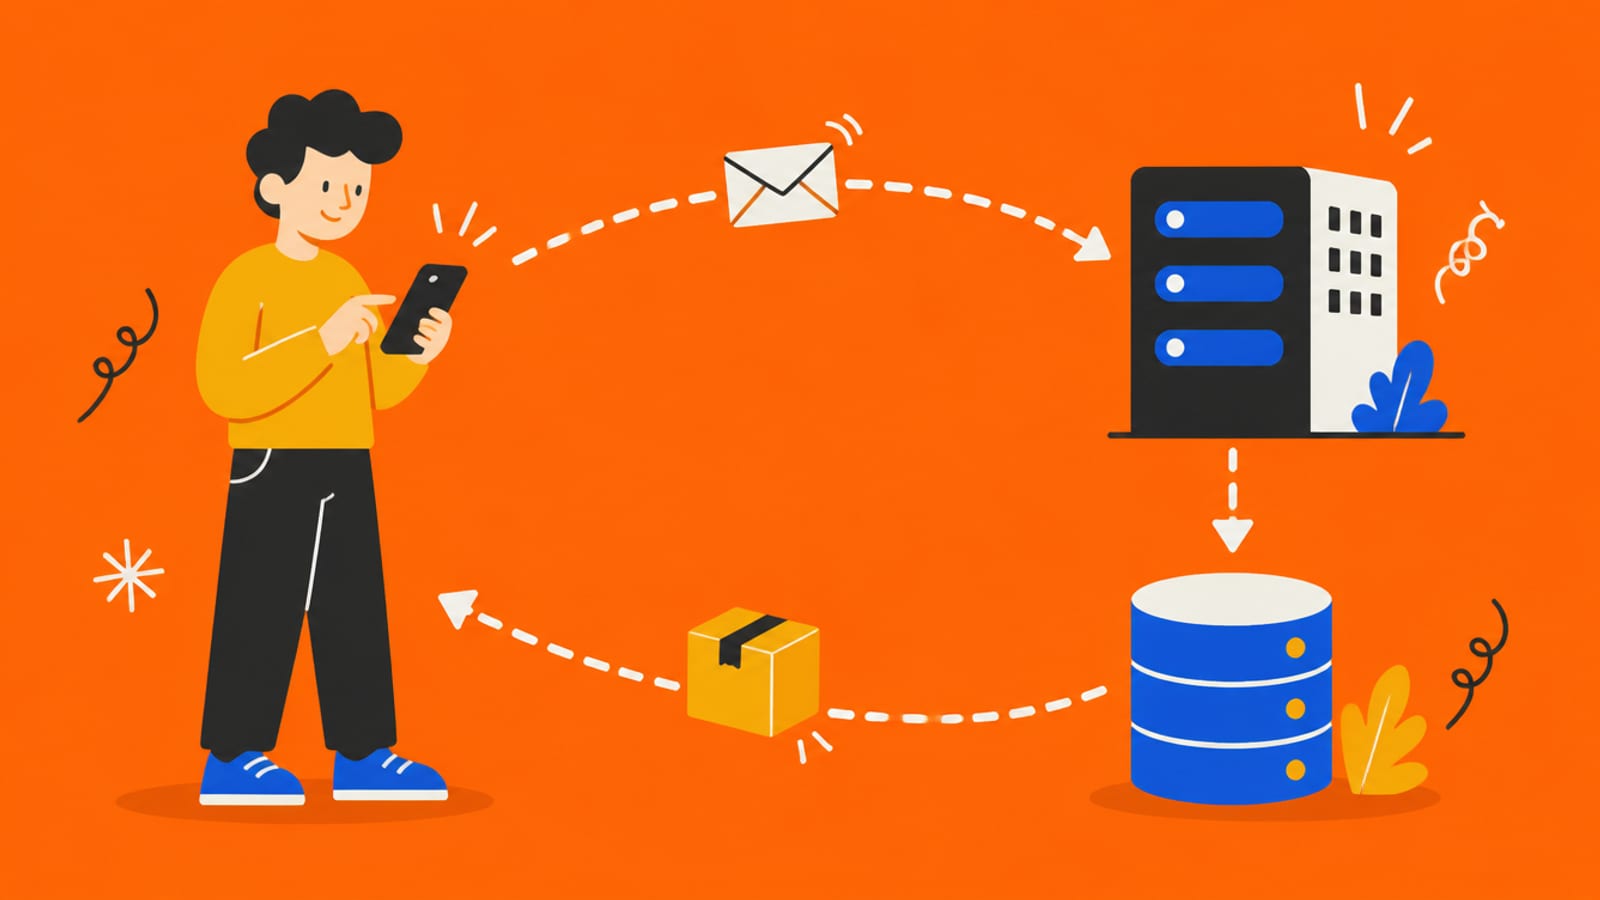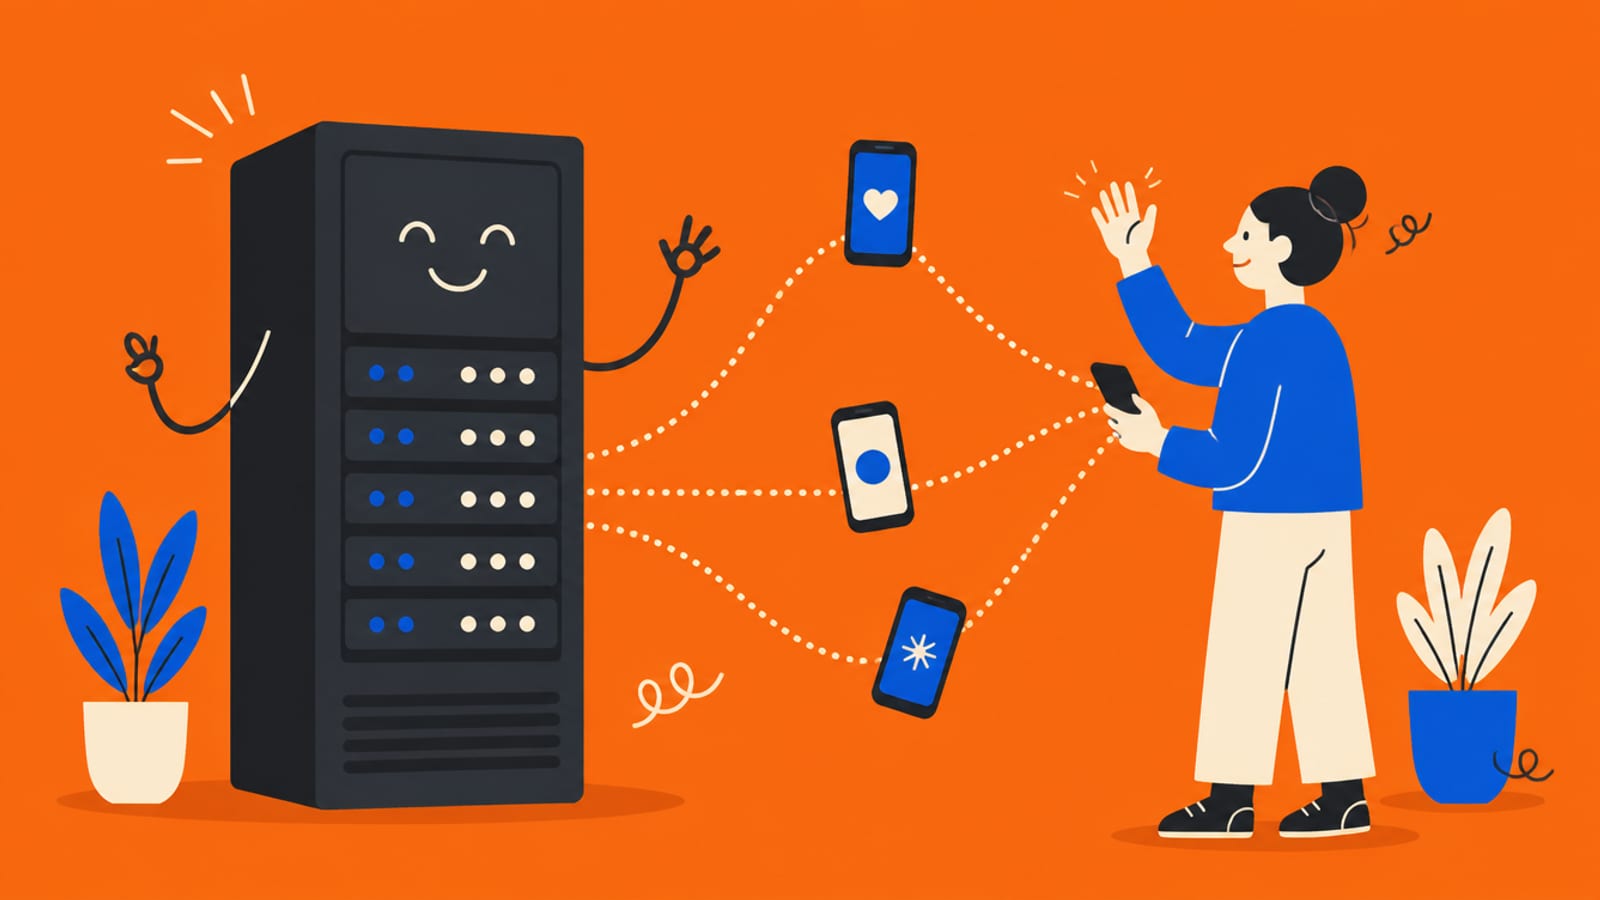
Where does the Sign up request actually land? Tap the building in the journey and look inside.
The server is where your app's real logic lives — the only place your password is checked.
Tap the button, then tap each stop
What the server can see
Your email and password, briefly, in memory — this is where the app checks them, hashes the password, and decides what you're allowed to do. Secrets that live HERE stay private.
It lands on a server: a computer that's always on, somewhere else, waiting for requests.
MDN: "A server is a software or hardware offering a service to a user, usually referred to as client." The word means both the machine and the program answering on it.
Physically, it's usually one of thousands of computers in a data centre, rented by the hour or by the request. You'll never see it.
- Receive
The full request: address, labels, contents
- Check
Who is this? Are they allowed? Too many?
- Do the work
Read or save data, call other services
- Answer
Send the response back
- Receive
The full request: address, labels, contents
- Check
Who is this? Are they allowed? Too many?
- Do the work
Read or save data, call other services
- Answer
Send the response back
The server sees everything in the request. Your users can't see inside the server. That one-way glass is why secret keys belong here, never on the phone.
"Serverless" still runs on servers. The platform just starts your code when a request arrives, so you don't manage the machine.
Try it with the rules off. In the sandbox, take the server out of the journey and wire the phone straight to the database. Then try asking for rows that aren't yours, with the rules on and then off.
Check yourself
0/4 got itSaved on this device only. No account, no streaks.
Next in the journey of a tap: What is an API?.