You built it vibe coding on Lovable, Bolt, Replit or v0, with Supabase and Vercel underneath, and a security questionnaire just asked for SOC 2. Each platform's own report, how to get it, which plan it sits behind, whether it trains on your data, and the half of the audit that is still yours.
The email usually arrives right after a good demo. The buyer liked the app. Then procurement sends a spreadsheet, and row 12 asks: "Do you have a SOC 2 Type II report?"
You built the app in Lovable, Bolt, Replit or v0. It runs on Supabase and Vercel. Those companies all say they are SOC 2 compliant. So are you?
No. And the gap between their report and your app is exactly where buyers look. This page goes platform by platform through what each builder tool says on its own trust, docs and pricing pages: its SOC 2 and ISO 27001 status, how you get the report, which plan it sits behind, whether it trains on your data, and what it says stays your job.
We have skin in this. aliteq is vibe coded too. It runs on Cloudflare Workers with its content in Supabase. We have never been through a SOC 2 audit and we do not have a report. So read this as one builder's notes on the same stack you use, not an auditor's opinion.
Does building on Lovable or Supabase make my app SOC 2 compliant?
No. A platform's SOC 2 report covers that platform's controls, not yours. Supabase says it outright: its SOC 2 compliance "does not transfer to environments outside of the Supabase product or Supabase's control." Your app, your settings and your team are outside that line.
Supabase's SOC 2 page goes further: "If a customer needs to be SOC 2 compliant, they should themselves implement the requisite controls and undergo a SOC 2 audit." Every other platform here says a version of the same thing.
What their reports are good for is evidence. When you get your own audit, your auditor will want to see that you checked your vendors. Their reports go in that folder. The SOC 2 for AI startups guide explains how that vendor review works and what the whole audit costs.
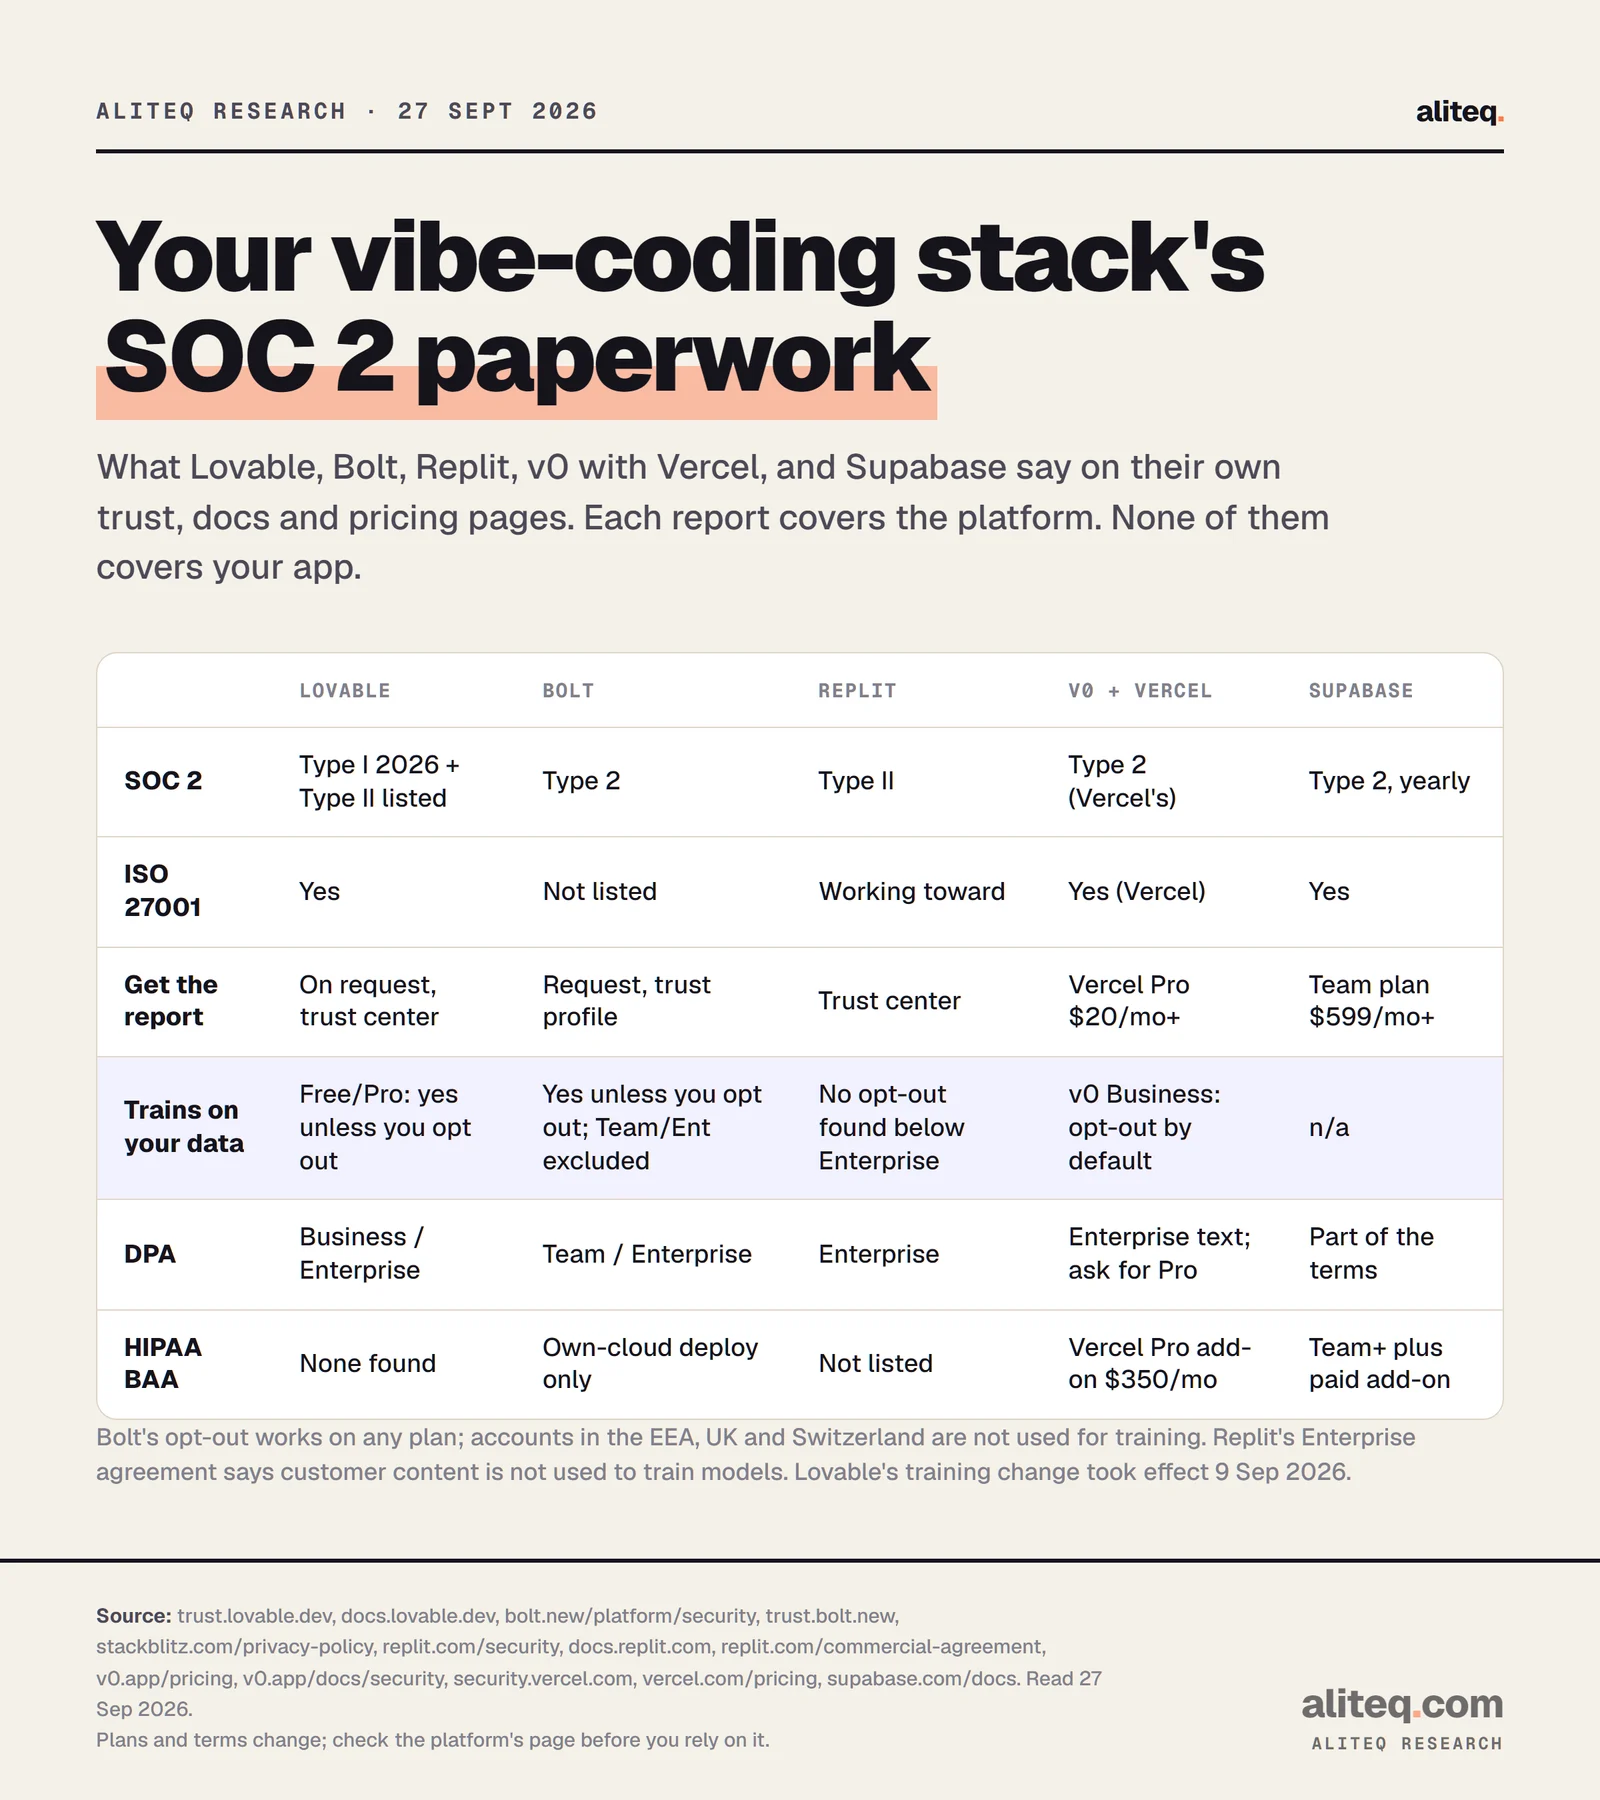
Each platform's own words, read on 27 Sep 2026. Their report covers them, not your app. · aliteq research
One word to watch. Several platforms say they are SOC 2 "certified." SOC 2 is not a certificate. It is a CPA firm's report, called an attestation, on a set period. When a buyer asks, they want the report, its type and its dates.
Lovable SOC 2: what the trust center shows
Lovable lists a SOC 2 Type I dated 2026 and a SOC 2 Type II on its trust center, plus ISO 27001:2022 and AIUC-1. The Type II report is available to customers on request through that trust center. The DPA and the no-training default come with the Business plan, $50 a month, or Enterprise.
The details, from Lovable's own pages:
SOC 2. The trust center lists "SOC 2 Type I - 2026," "SOC 2 Type II" and a bridge letter. A 10 June 2026 post says the Type I was "signed by Prescient Assurance" and that "the Type 2 will hit the Trust Center by end of August if everything plays well." When you request it, ask which audit period the Type II covers.
What it covers. The FAQ says the annual SOC 2 Type II covers "the AICPA Trust Services Criteria for Security." That is the one required category. If your buyer asks about Availability or Confidentiality, that is a separate question.
Getting the report. "The most recent SOC 2 Type II report is available to customers upon request through the Lovable Trust Center."
DPA. "If you're on a Business or Enterprise plan, your usage includes our Data Processing Agreement (DPA)."
AI training. Since 9 September 2026, Lovable may use Free and Pro plan data, including prompts, code and project files, to train models unless you opt out in account settings. Business and Enterprise workspaces are excluded by default. The opt-out page notes that opting out does not pull back data already used.
HIPAA. We found no BAA. Lovable's terms say not to upload health data covered by HIPAA unless your plan or a written agreement allows it.
What stays yours. Lovable's security docs are plain: "You are responsible for ensuring that your app meets the security requirements appropriate for its use case." The Lovable app checks before you share it are the place to start.
Bolt SOC 2: what StackBlitz says
Bolt says it "is SOC 2 Type 2 certified," with a "Request the SOC 2 report" button on its security page. Its trust profile does not list ISO 27001. Bolt trains on your data unless you opt out, on any plan. Team and Enterprise customers under an MSA or DPA are excluded.
SOC 2. The trust profile lists SOC 2 Type 2, GDPR and CCPA. A February 2026 update there said the Type II report "will be available at the end of the 2nd quarter of 2026." The profile does not show the auditor or the audit period, so ask for both.
Getting the report. Request it on the trust profile. Its policies (incident response, access control, data retention and more) are also listed there, each behind "Request access."
AI training. StackBlitz's privacy policy, updated 22 September 2026, lets it use Bolt content to train and improve AI models unless you opt out. You can opt out in account settings or by emailing StackBlitz, free and on any plan. Accounts located in the EEA, UK and Switzerland are not used. Organization-managed accounts are excluded unless the admin turns it on.
DPA. The security page ties the training exclusion to "Enterprise and Team customers under an MSA or DPA." Teams lists at $30 per member a month.
HIPAA. The only HIPAA mention is for running Bolt inside your own AWS or Azure account, an Enterprise deployment. We found no BAA for the standard plans.
What stays yours. Bolt's security page does not publish a shared-responsibility split. The line still exists. The Bolt app checks before you share it cover the parts that land on you.
Replit SOC 2: Type II, ISO 27001 still in progress
Replit says: "Replit holds SOC 2 Type II certification. We also comply with GDPR and are working toward ISO 27001 certification." It points buyers to its trust center. Its DPA and its promise not to train on customer content sit in the custom-priced Enterprise agreement.
SOC 2. Confirmed on Replit's security page and in its docs. Replit sends reports through its trust center at trust.replit.com. That page blocked our reader, so we cannot tell you its access terms, auditor or audit period. Ask when you request it.
ISO 27001. Not yet. Replit's own words are "working toward."
DPA. Replit's DPA "forms part of and is incorporated into the Replit Commercial Agreement," which is its Enterprise agreement.
AI training. The Enterprise agreement says Replit "will not use Customer Content to develop or improve Replit's products or services, train machine learning models, or create derivative works, except as expressly permitted in this Agreement." We found no matching opt-out for the Core ($20 a month) or Pro ($100 a month) plans in the privacy policy.
AI inside your app. If your Replit app calls models through Replit's AI Integrations, the docs say paid model endpoints do not train on your data, while free endpoints may train on your prompts and completions. Enterprise is limited to zero-data-retention endpoints. A buyer who asks "where do our prompts go?" is asking about this.
What stays yours. Replit publishes the clearest split of any platform here. Its shared responsibility model puts on your side: your app code and business logic, reviewing the Agent's output, vetting dependencies, testing your app, managing secrets, access control and user management, and regulatory compliance, from GDPR to HIPAA. The Replit app checks walk through them.
v0 and Vercel SOC 2: one report, two bills
v0 has no separate report. "v0 is included in Vercel's SOC 2 Type 2 attestation for Security, Confidentiality, and Availability." Vercel's 2026 Type 2 was done by Schellman and covers 1 July 2025 to 30 June 2026. You get it from Vercel's trust portal on a Vercel Pro ($20 a month) or Enterprise plan.
The report. Vercel's trust center says the 2026 report "was completed by Schellman and covers our audit period July 1, 2025 to June 30, 2026." It also lists ISO 27001:2022, a SOC 3 and a HIPAA report.
Getting it. Vercel's pricing page says "Security collateral available for Pro and Enterprise plans." Hobby accounts do not get it.
AI training in v0. v0 bills separately from Vercel hosting. Its pricing lists "Training opt-out by default" on Business, $100 per user a month, and "Your data is never used for training" on Enterprise. Free and Plus ($30 per user a month) list neither.
DPA. Vercel's published DPA is written for its Enterprise terms. If you are on Pro, ask Vercel which DPA applies before you tell a buyer you have one.
HIPAA. Vercel sells a BAA as a Pro add-on at $350 a month. Hobby cannot get one.
What stays yours. Vercel's shared responsibility page says customers decide whether its platform meets "the specific needs and requirements for their application." In practice that means your environment variables, your team's access and whatever v0 wrote. The v0 app checks cover the common gaps.
Supabase SOC 2: the report sits behind Team
Supabase has a SOC 2 Type 2, audited yearly on a 1 March to 28 February window, and ISO 27001. The report is only for Team and Enterprise customers, from the Legal Documents section of the dashboard. Team starts at $599 a month. On Free or Pro you cannot download it.
DPA. Part of Supabase's terms of service, so every customer has one.
AI training. Not a model vendor, so the question does not apply.
HIPAA. "You will need to be at least on the Team Plan to sign a BAA with us." It also needs a paid HIPAA add-on, and Supabase does not publish that price.
What stays yours. Supabase is the most specific. From its shared responsibility model: "You are also responsible for ensuring that tables with sensitive data have the right level of access. You are also responsible for managing your database secrets and API keys, storing them safely in an encrypted store." It recommends "that you always apply Row Level Security (RLS)" and says acting on its Security Advisor alerts is your job.
One more line from its SOC 2 page matters for audits: "Supabase sets Postgres connection logging to off by default for new projects." If your auditor wants connection logs, you have to turn logging on and decide how long to keep them. If RLS is new to you, read what Row Level Security does first.
Cursor, if you build in an editor
Cursor is a code editor, not where your app runs, but buyers sometimes ask about it. It holds a SOC 2 Type II, ISO 27001:2022, ISO 42001 and AIUC-1. Reports are "available on request at trust.cursor.com." Cursor trains on your code unless Privacy Mode is on.
Its trust center posted an updated SOC 2 Type 2 report on 4 September 2026. Privacy Mode "is available to anyone (free or Pro)," and with it on, "we will not train on your data." With it off, Cursor's data-use page says it may use your code and prompts to train its models. Its trust center also has a HIPAA guide for Enterprise customers who want a BAA. For what to check in code you wrote with it, see the Cursor pre-ship checks.
What their SOC 2 does not cover in your app
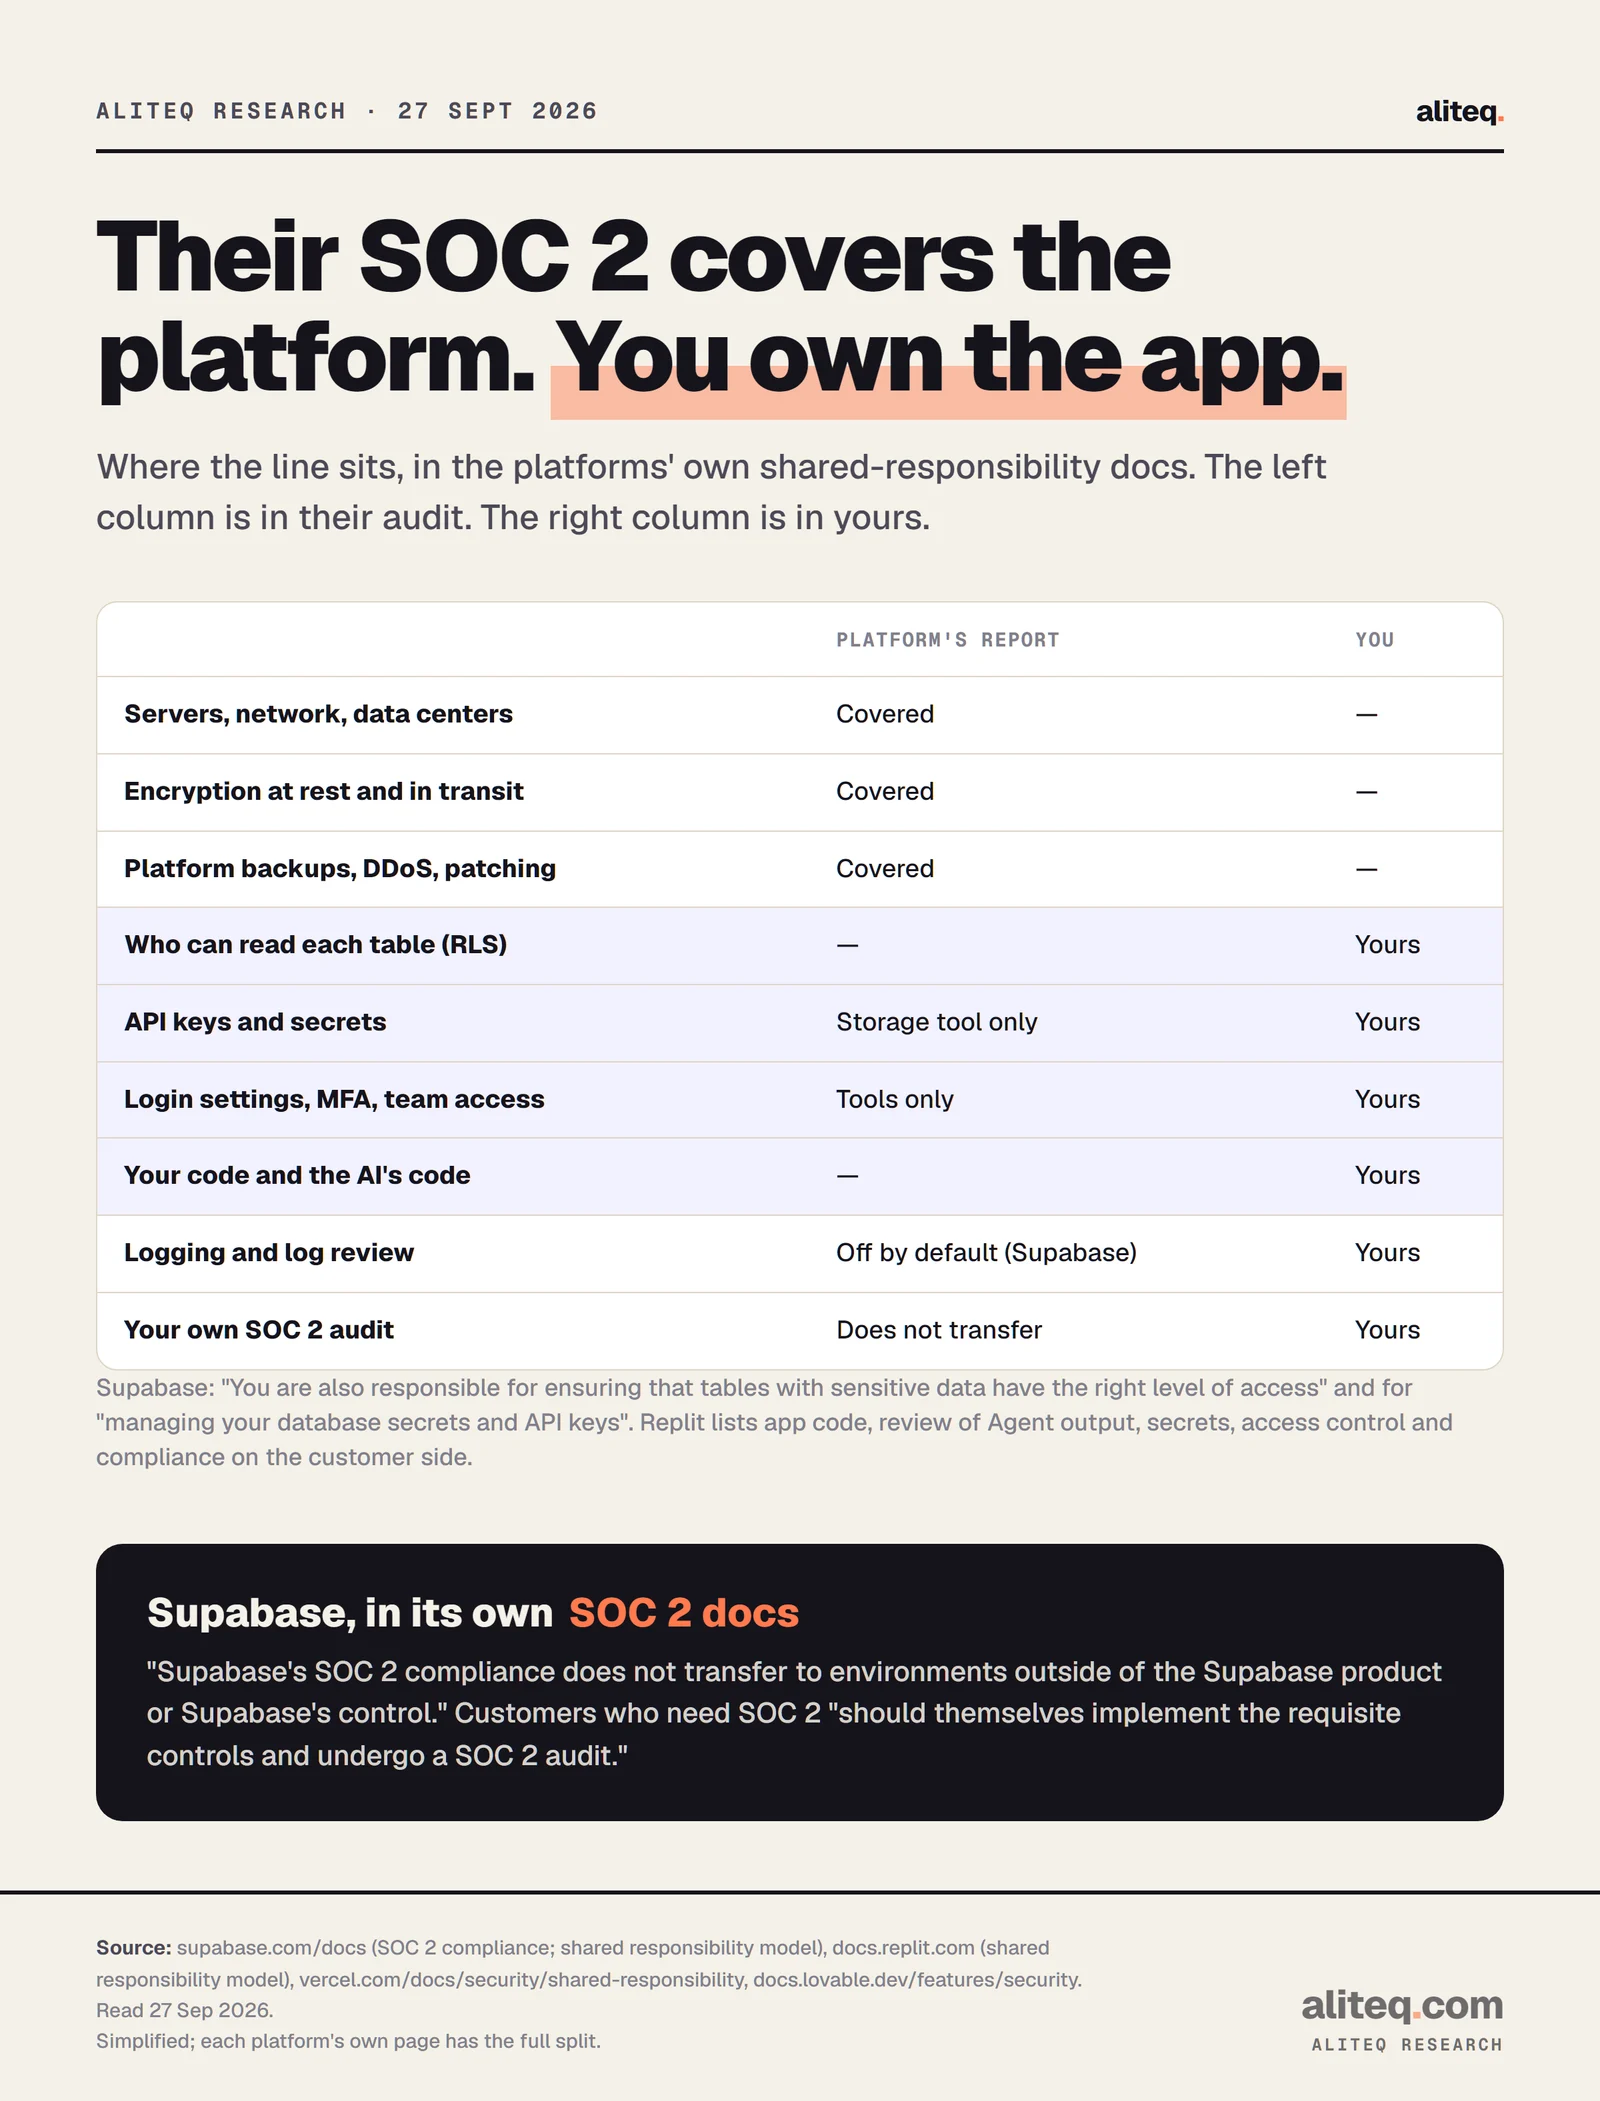
Their audit tested their servers, their encryption, their backups and their staff. It did not test anything you configured. That means your database access rules, your keys, your login settings, your team's accounts, your code, and the code the AI wrote for you.
Simplified from Supabase, Replit, Vercel and Lovable's own shared-responsibility docs. · aliteq research
This is where vibe-coded apps usually fall short, and it is what a security questionnaire actually probes:
Who can read each table. On Supabase, that is your Row Level Security policies. A platform report cannot vouch for a policy you wrote, or one you never turned on. See RLS, explained.
Login settings. Whether sign-up is open, whether email is confirmed, whether your admin accounts use multi-factor login.
Your team's access. Who has access to the Lovable workspace, the Supabase project and the Vercel team, and whether someone who left still does.
Your code, and the AI's code. Replit says reviewing its Agent's output is your job. The same holds for every tool here.
Logs. Whether you keep any, and whether anyone reads them.
The six checks before you share a vibe-coded app cover most of this list in an afternoon. None of it needs an auditor. All of it is what a buyer's questionnaire will ask about.
What it costs to get the paperwork
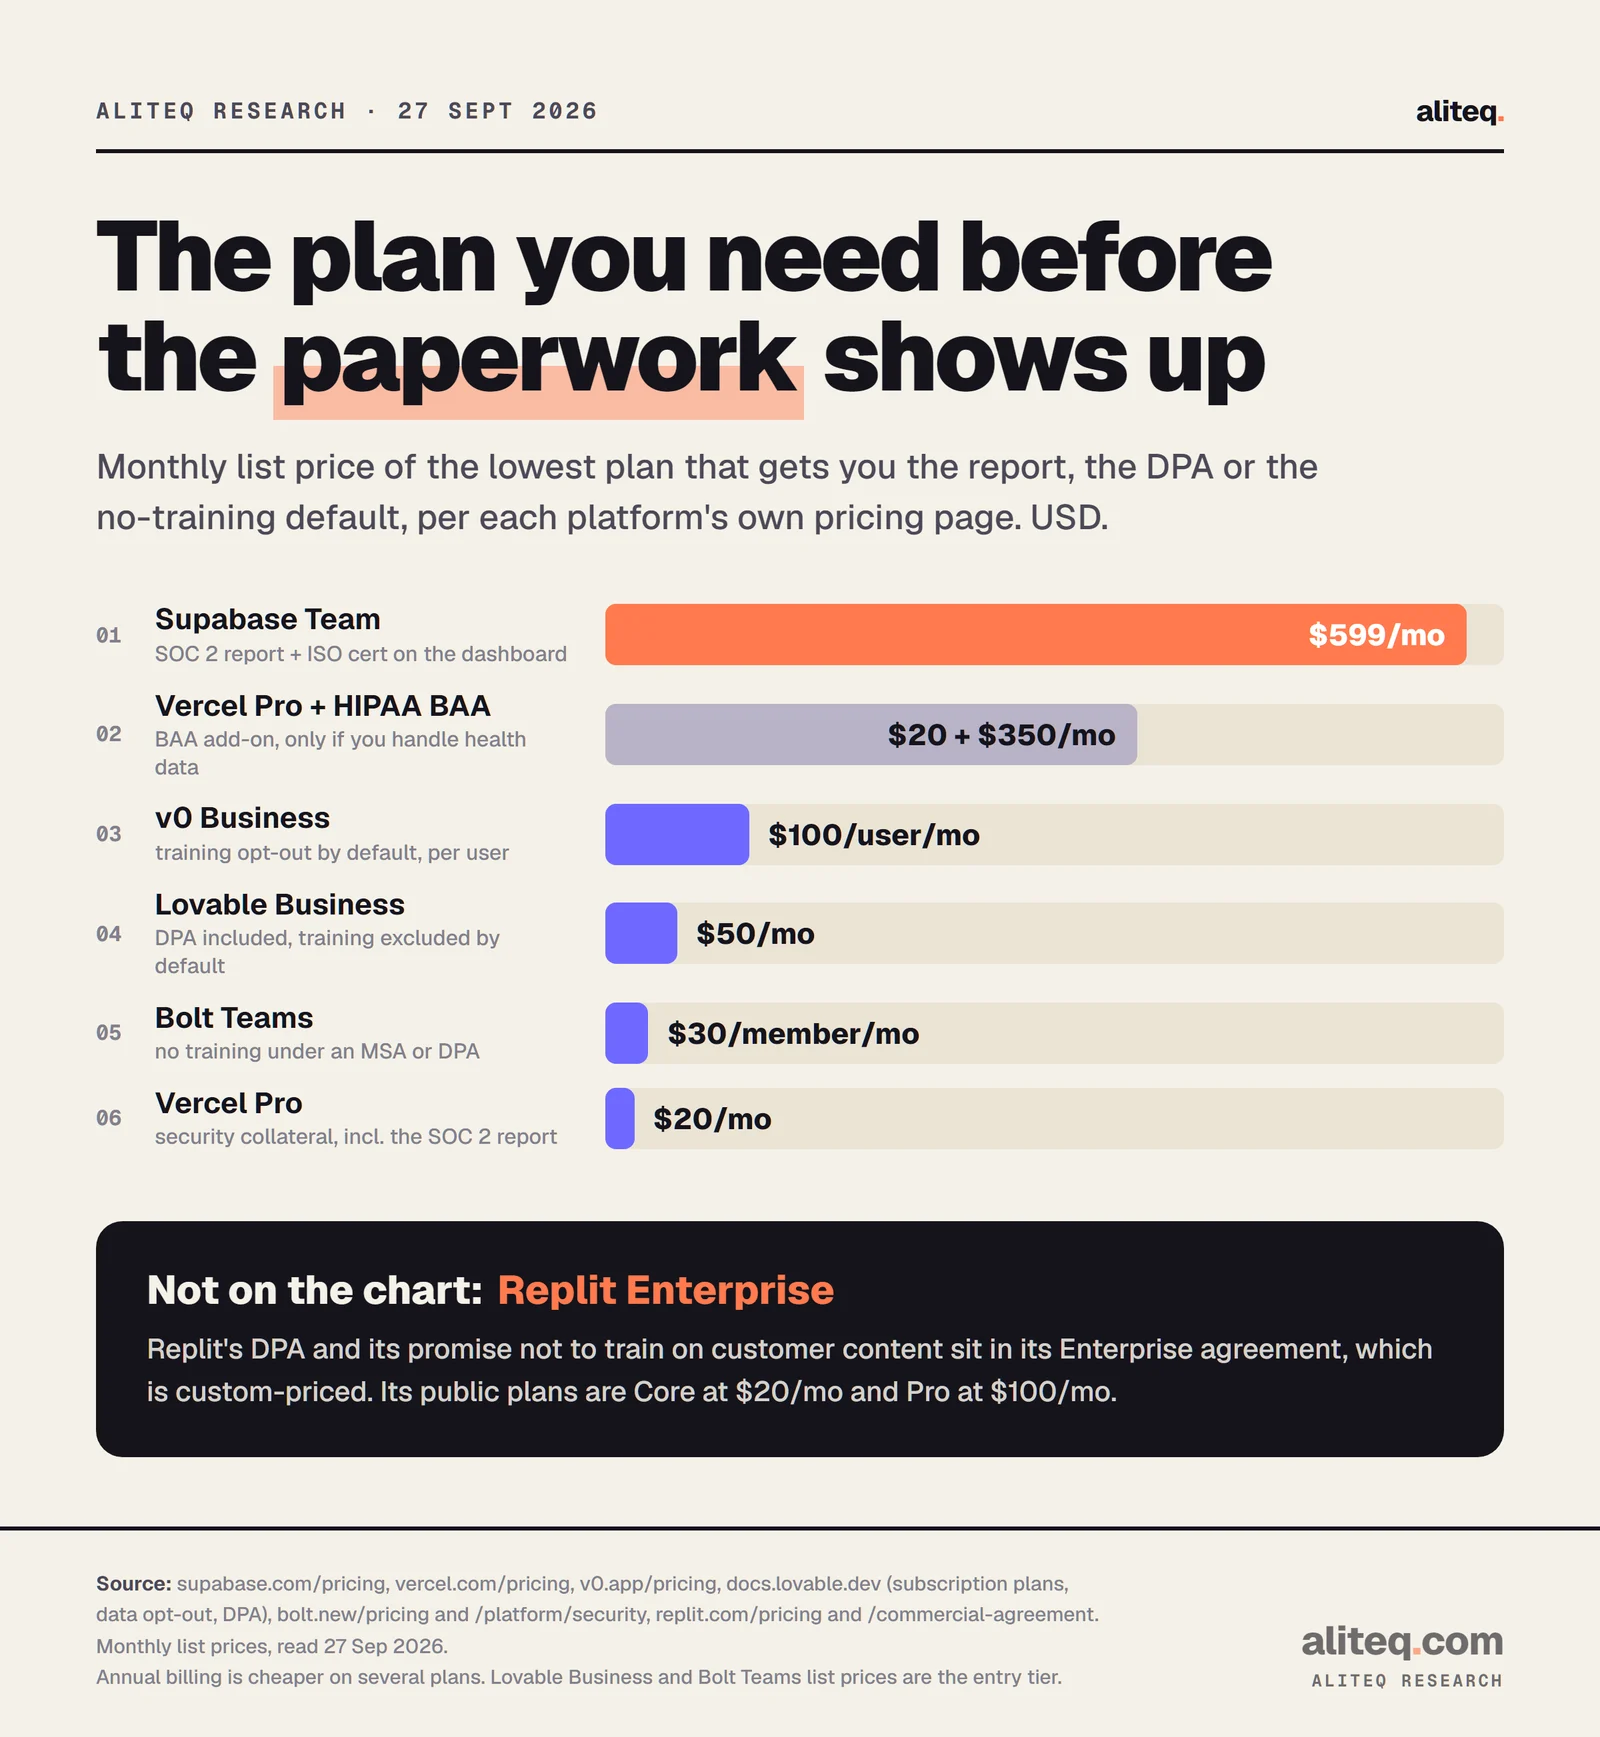
Before any audit, you may need a higher plan just to hold your vendors' reports and terms. Supabase Team is $599 a month. Vercel Pro is $20. v0 Business is $100 per user. Lovable Business is $50. Bolt Teams is $30 per member. Replit's DPA sits in custom-priced Enterprise.
Monthly list prices on each platform's pricing page, 27 Sep 2026. Annual billing is cheaper on several. · aliteq research
You do not need all of them. Upgrade only where a buyer's question requires it. If the questionnaire asks for your vendors' SOC 2 reports, the Supabase line is the big one. If it asks whether your AI tools train on customer data, the Lovable, Bolt or v0 line matters more.
Those upgrades are the small part. If the buyer wants your own SOC 2, the audit, a compliance platform and a pen test cost far more. The calculator below starts from a tiny team. It includes the stack upgrades as an optional line, so tick the ones you need and see the first-year total.
SOC 2 cost + timeline estimator
Year one
$26.4k–$62k
Year two and later: roughly 40–70% of year one (vendor-reported).
Time to report
9–15 months
Includes the 6-month window. There is no AICPA minimum; 3 months is the practical floor.
Audit fee
1–10 people, simple systems
$7k–$10k
Compliance platform
Vanta/Drata-class, per year
$12k–$28k
Pen test
basic
$5k–$15k
Readiness assessment
skipped
—
Stack upgrades
none selected
—
Your team's time
40–150 h × $60/h
$2.4k–$9k
Ranges from SOC2Auditors.org (directory), Vendr (buyer data), Drata, The Pun Group (CPA firm), Fractional CISO, SecureLeap and Cherry Bekaert (CPA firm); stack prices from Supabase, Vercel and Lovable pricing pages. Checked 27 Sep 2026. Most are published by companies that sell audits or compliance software. An estimate, not a quote.
You can answer honestly without a report of your own. Say what you have, attach your vendors' evidence, and show the controls you run. Many buyers accept that from a small company, at least for a first deal. Never write "yes" to "Do you have a SOC 2?" because your platform does.
Ask the buyer what they need: your own SOC 2 report, or proof your vendors have one. Many first deals only need the second.
Request each platform's report from the pages above and note its type and audit period. Upgrade only where the report sits behind a plan.
Turn off AI training where you can: opt out in Lovable, Bolt and Cursor, or move to the plan that excludes you by default.
Run the six app checks: RLS on every table, no secret keys in the browser, sign-up and login locked down, team access reviewed.
Write one page on how you build: who can deploy, how AI-written code gets reviewed, where logs go. Buyers ask for it.
If the buyer truly needs your own SOC 2, price it now. A first Type 2 takes months, so give them a date, not a promise.
Lovable's own trust center has a line worth copying for that one-pager. It says management "performs reviews of SOC 2 reports from service providers at onboarding and annually." That is the vendor review a buyer wants to see from you too.
Quick answers
Is Lovable SOC 2 compliant?
Lovable's trust center lists a SOC 2 Type I dated 2026 and a SOC 2 Type II, plus ISO 27001:2022. The Type II report is available to customers on request through the trust center. It covers Lovable's platform, not the app you build on it.
Does Supabase's SOC 2 cover my app?
No. Supabase says its SOC 2 compliance does not transfer outside its product or its control, and that customers who need SOC 2 must implement their own controls and get their own audit. Your RLS policies, keys and access settings are your responsibility.
How do I get Supabase's SOC 2 report?
Only Team and Enterprise customers can download it, from the Legal Documents section of the organization dashboard. Team starts at $599 a month. Free and Pro projects do not get the report.
Is v0 SOC 2 compliant?
v0 is included in Vercel's SOC 2 Type 2 attestation for Security, Confidentiality and Availability. Vercel's 2026 report covers 1 July 2025 to 30 June 2026, and its security collateral is available on the Pro and Enterprise plans.
Do Lovable, Bolt, Replit and v0 train on my code?
It depends on the plan. Lovable trains on Free and Pro data unless you opt out. Bolt trains unless you opt out, on any plan. v0 Business is opted out by default. Replit's Enterprise agreement says it will not train on customer content; we found no opt-out below Enterprise.
Can I say my app is SOC 2 compliant because my platforms are?
No. SOC 2 is a report a CPA firm issues about your company's controls over a set period. Your platforms' reports are evidence you checked your vendors. Say that, attach them, and describe the controls you run yourself.
The platforms did their audit. Yours is the app on top. For everything else on compliance, from the audit cost to the questionnaire, start at the Security & Compliance hub.
Use this in your own page
Teaching this? Paste the live version into your course, blog or answer. Free, no sign-up; the credit line links back here.